Security and sovereignty
Security and data sovereignty, in Europe
We prioritise data sovereignty, auditability and security. The platform was designed for those who must prove what they do with information.
How we protect the data
Data stays in the EU, encrypted, and only the people who need it can access it.
Each organization sees only its own data. A consultant can belong to several organizations by invitation, and the customer can refuse external members.
Role-based permissions, multi-factor authentication (authenticator app and FIDO2 keys), SAML SSO per organization and SCIM provisioning.
Every change is logged with user and date, in an immutable record. Administrators and auditors export an integrity proof that can be verified offline.
The infrastructure is monitored, with alerts when something looks abnormal.
In numbers
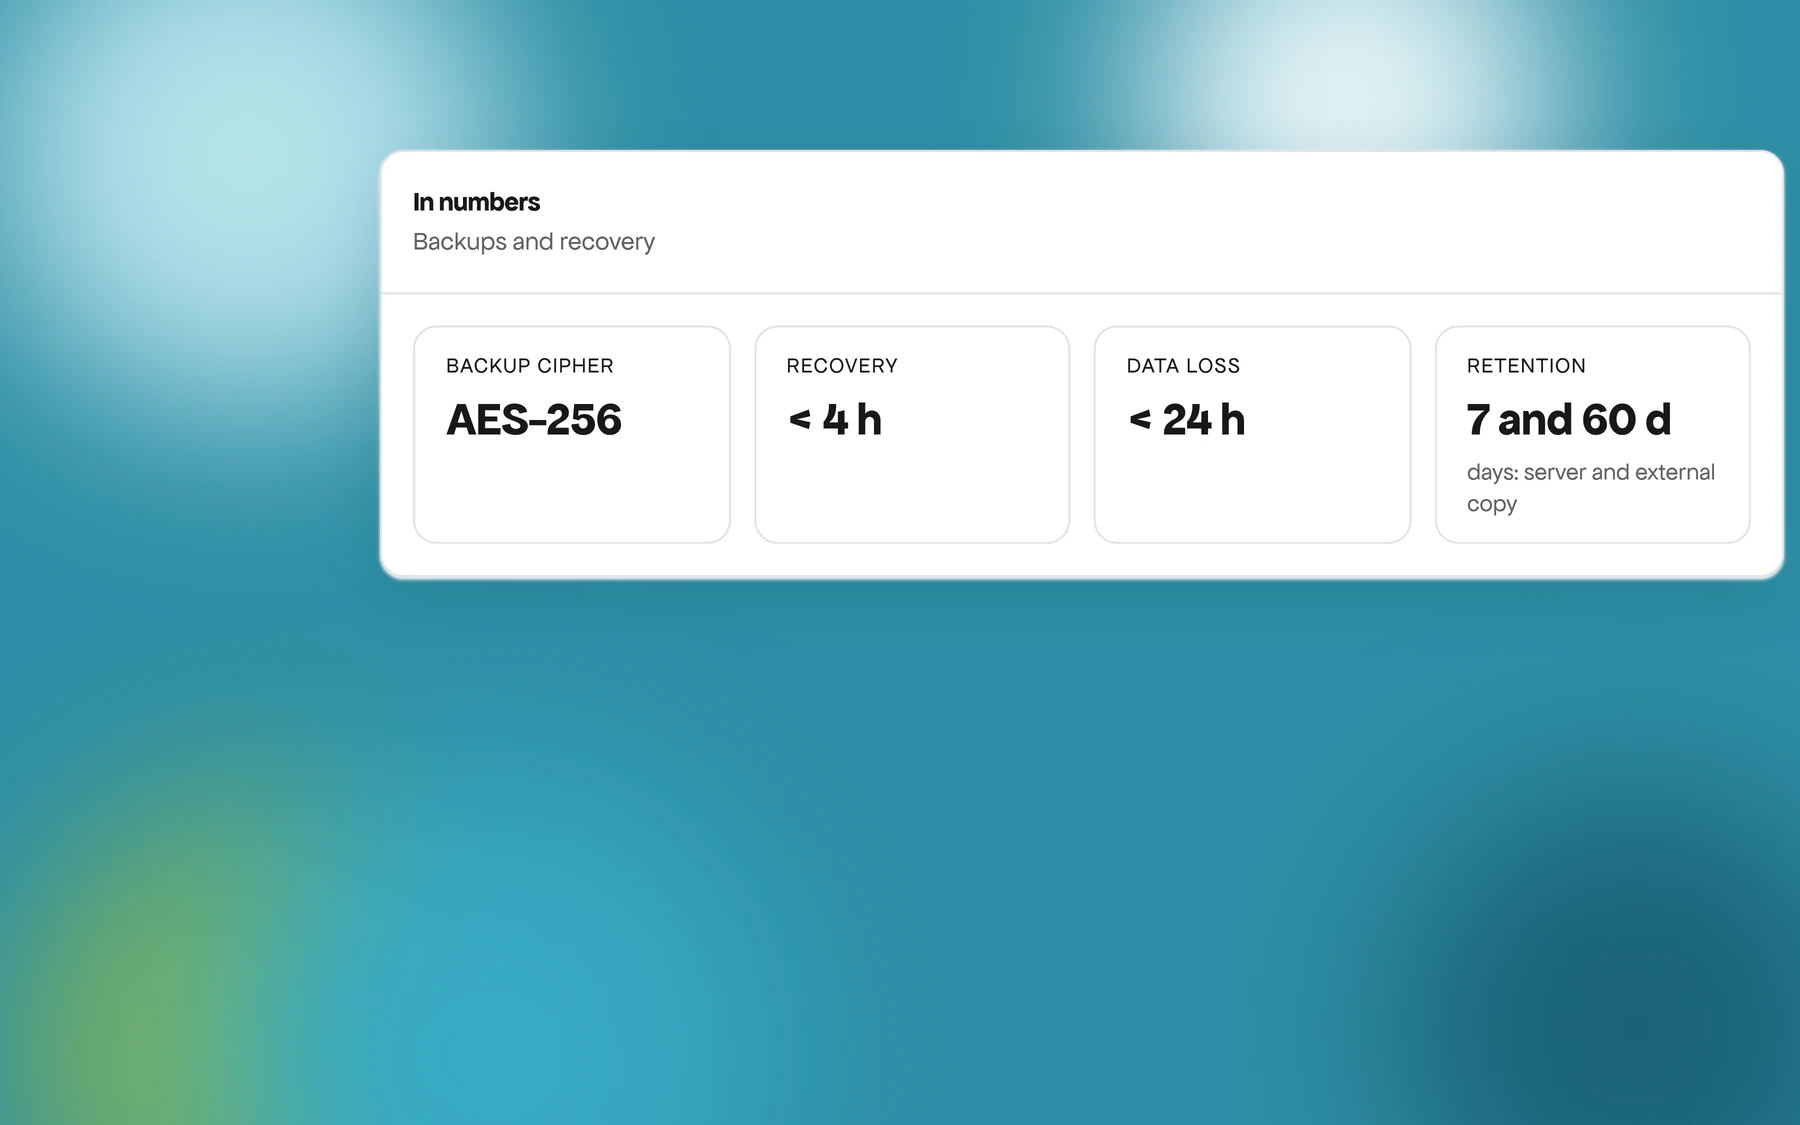
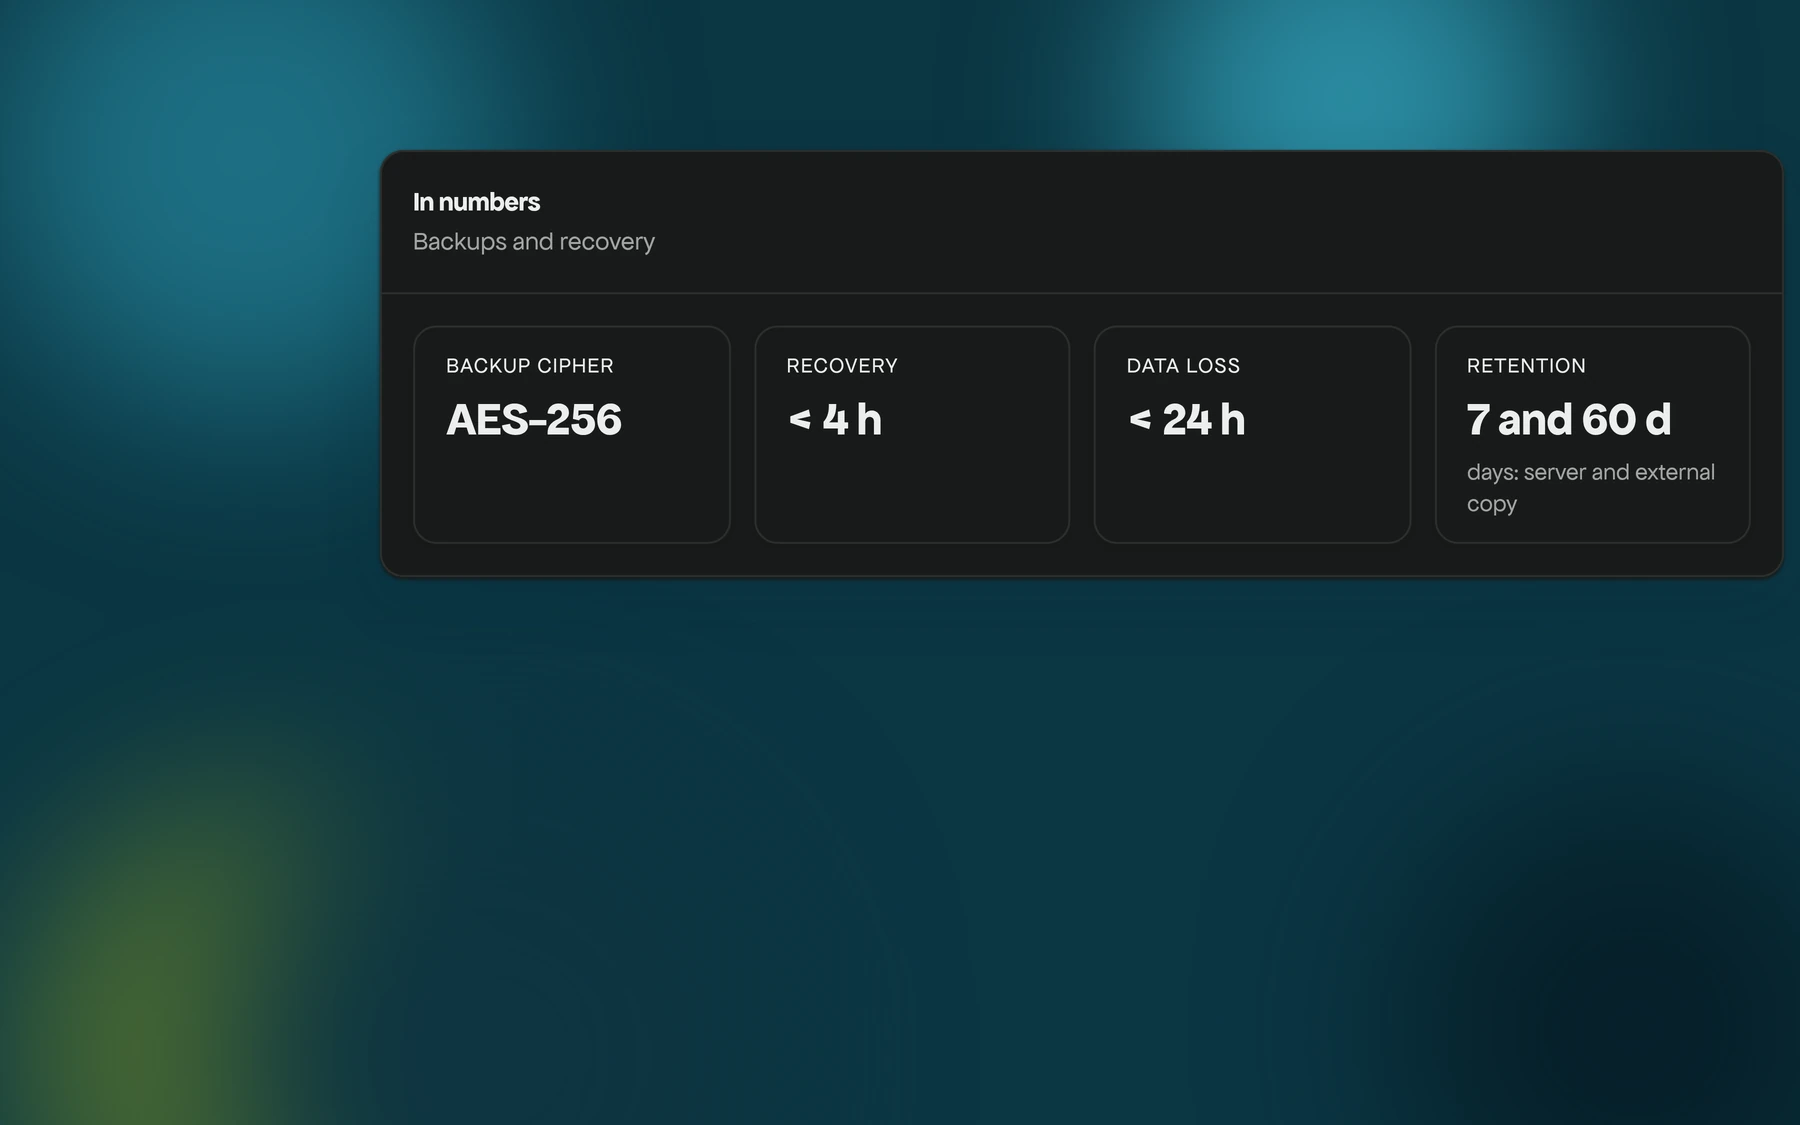
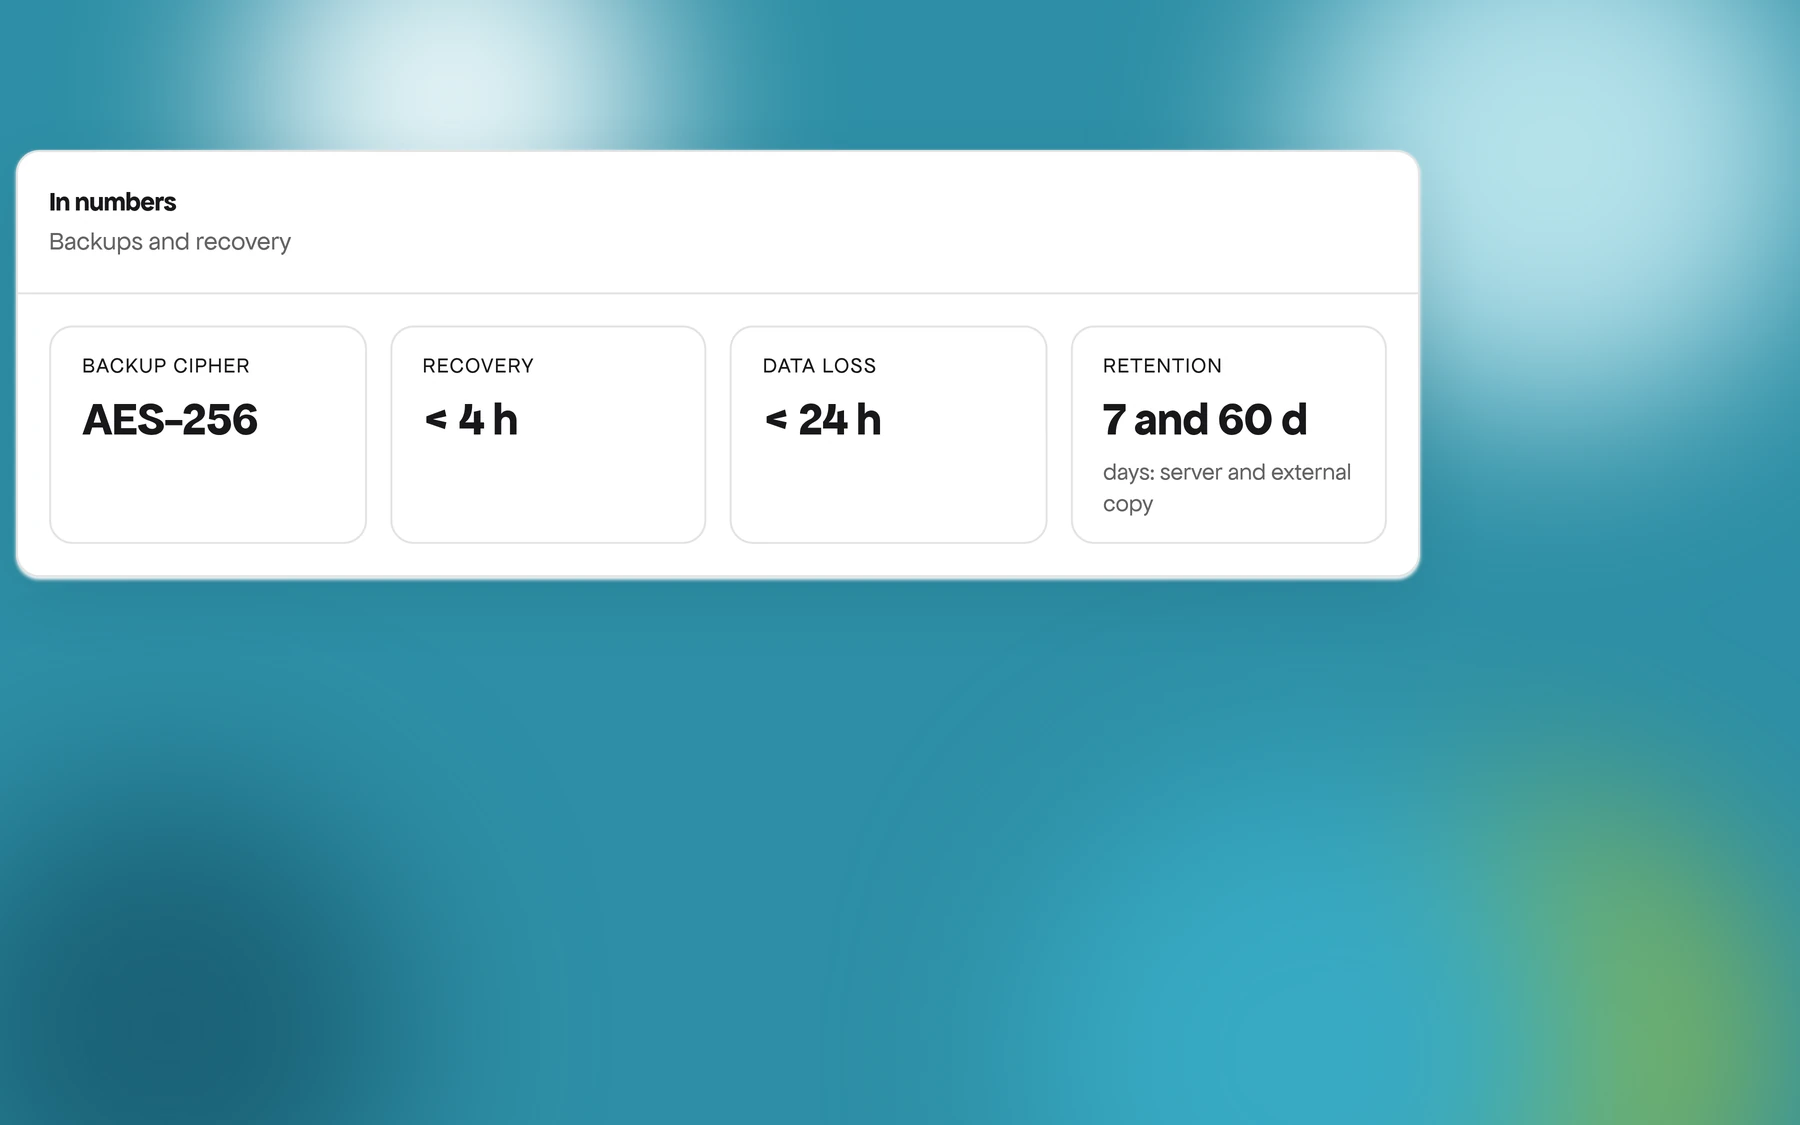
Encrypted copies every day, kept in two places, and a tested plan to get back online.
- AES-256
- Encryption of the daily backups
- < 4 h
- Full recovery objective (RTO)
- < 24 h
- Maximum data loss objective (RPO)
- 7 and 60 days
- Backup retention: 7 days on the server and 60 days in an external copy
AI prepares, the decision is yours
In form suggestions and assisted filling, only what you accept is saved; other analyses are marked as AI-generated, for you to review. For AI requests to providers outside the EEA, standard contractual clauses and zero-retention providers apply. You can switch AI off or use your own key.
The full documentation is public
Architecture, data processing agreement, service level and responsible vulnerability disclosure are in the documentation.
Have a security questionnaire to answer?
Tell us what you need and we reply with the right documents.