Security is not a feature. It is a requirement.
See here how EterShield handles your data, who can access it and what controls you have.
How your data is handled
We do not train on your data
EterShield does not train or fine-tune models on customer data, and the contract with the AI provider provides for zero retention of the data sent.
Encrypted in transit and at rest
Communication uses TLS 1.3, sensitive personal data is encrypted with AES-256-GCM and backups with AES-256 before they leave the server.
Your data stays yours
We process data to provide the service and do not use it to train AI models. Each organization sees only its own data and can export it.
Service status
The status page shows availability and incidents, with history and an RSS feed.
What you can read
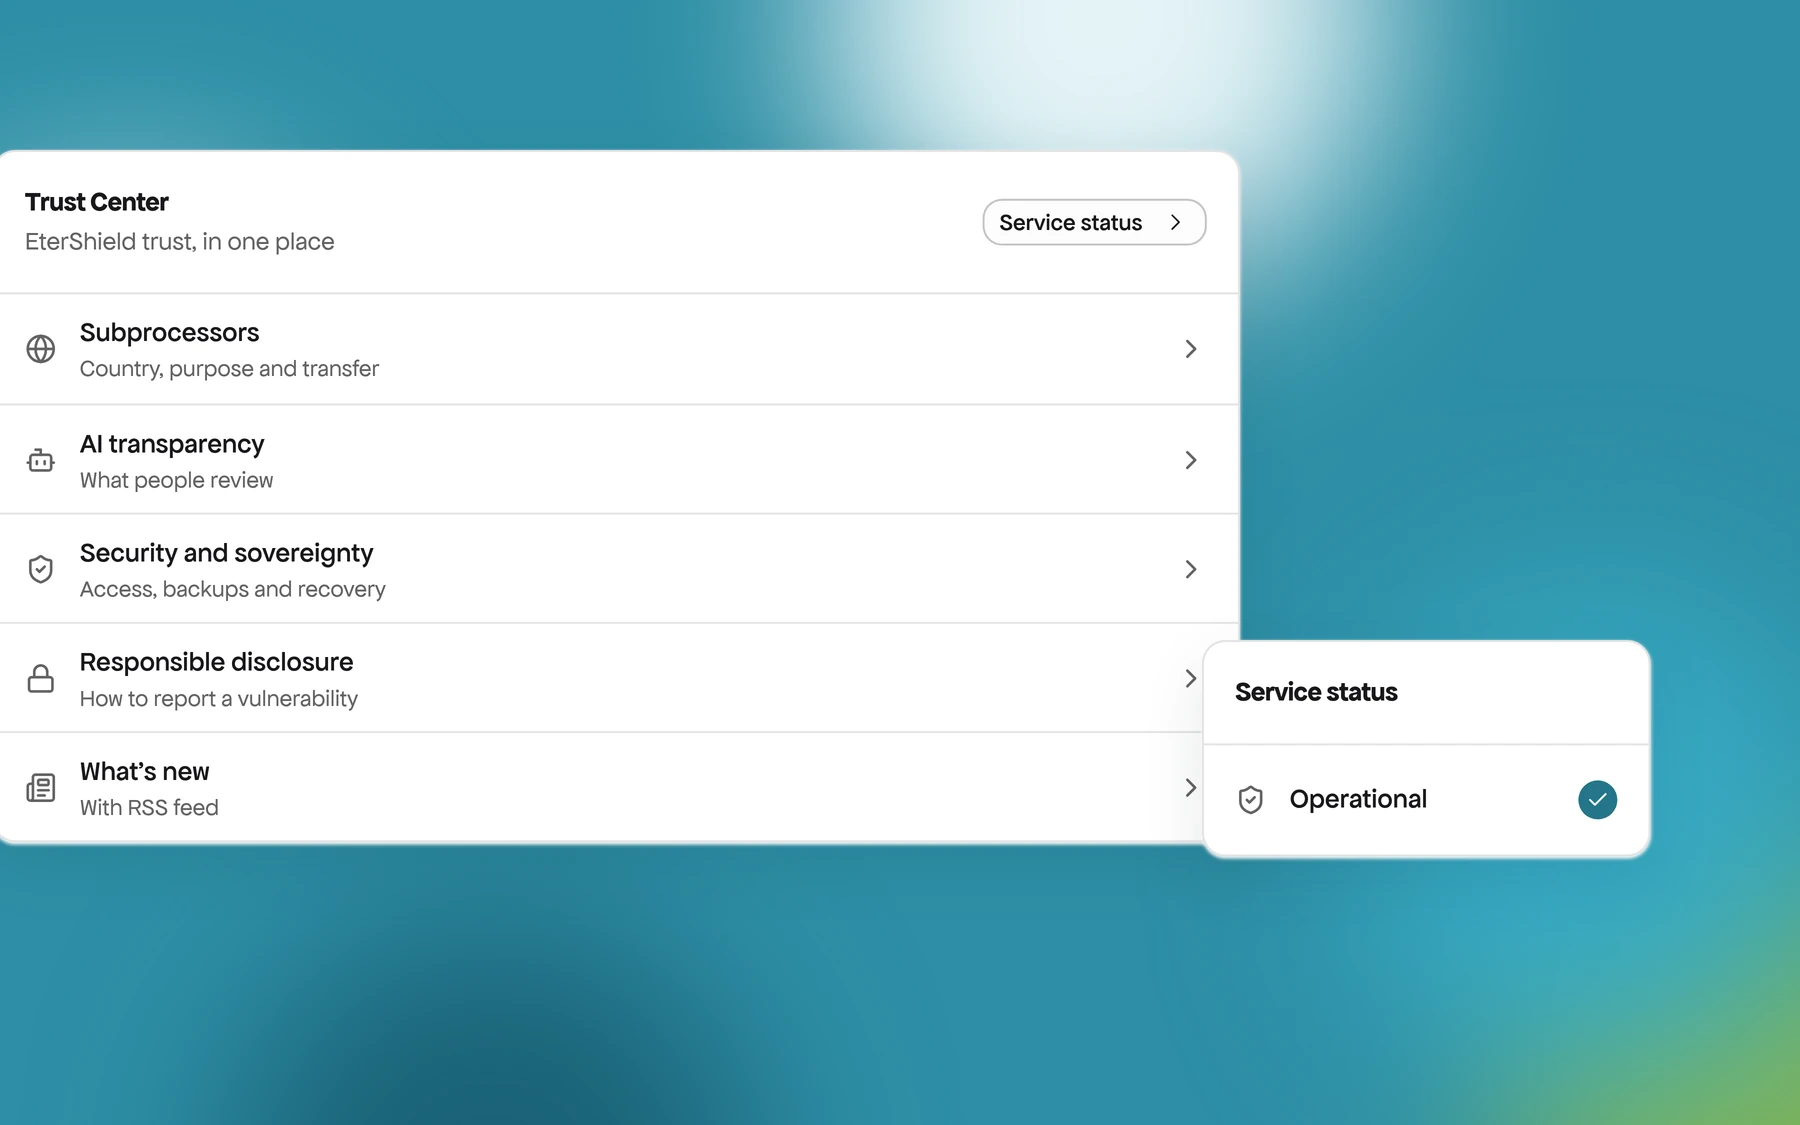
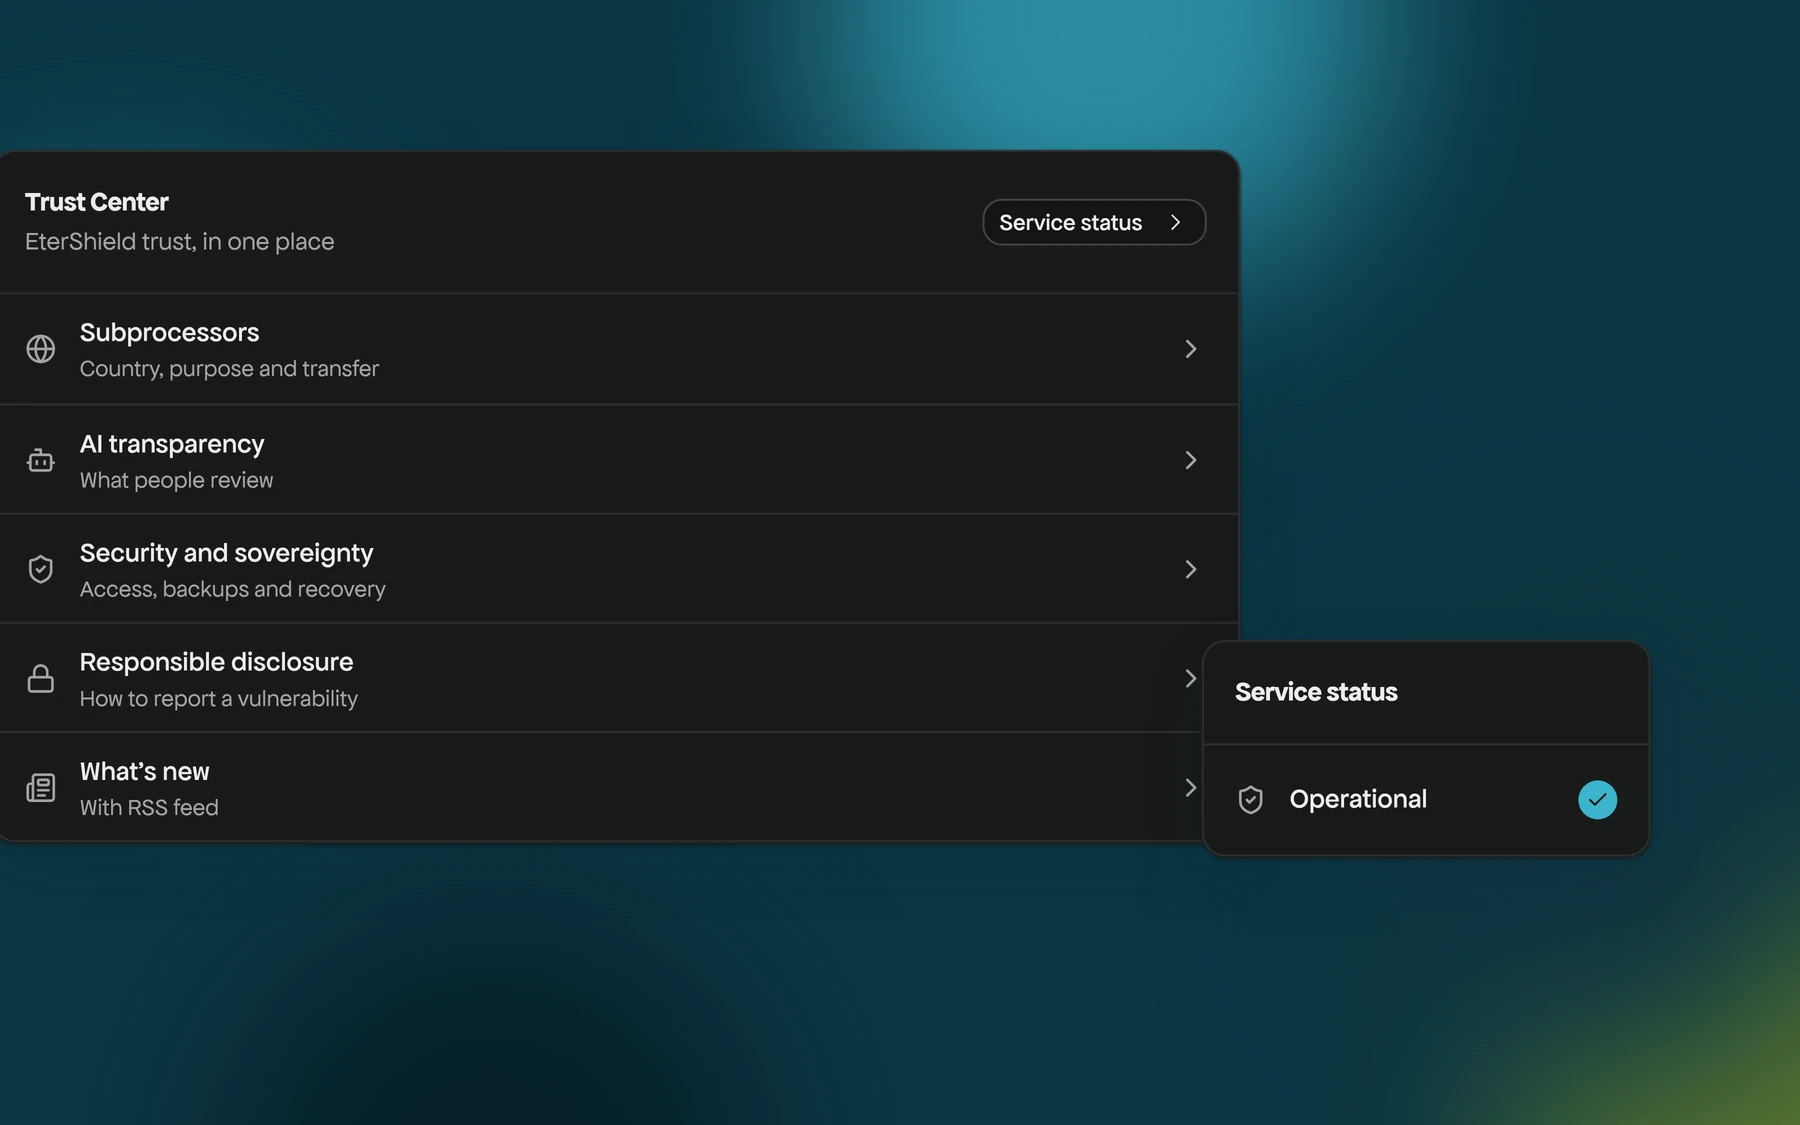
Who processes data on behalf of EterShield, with country, purpose and transfer basis. Subscribe to notices of changes.
OpenWhich model we use, where data stays, what people review and why we do not train on customer data.
OpenHow we protect data, access, backups and recovery.
OpenHow to report a vulnerability, the response deadlines and the acknowledgements.
OpenWhat changed in EterShield, with an RSS feed.
Open
Trust documentation
The DPA, the service level agreement (SLA), the transfer impact assessment (TIA) and the Security & Trust summary are in the public documentation.
Documents on request
You can ask for the DPA for signing and the security summary. The request reaches our team, which reviews it and replies by email. Nothing is downloaded automatically.
If you prefer, write to us at info@etershield.com.
Do you have a supplier questionnaire to answer?
Tell us what you need and we will reply with the right documentation.