Compliance
 Compliance lead
Know where the gaps are before the audit.
 Security team
Answer several frameworks without repeating work.
Assess the organization against the frameworks you care about and see the real status of each control. Know where the gaps are before the audit. Answer several frameworks without repeating work.
The module includes framework catalog and assessments, with a score calculated from the answers; status of each control, notes and evidence; gaps recorded by severity; aI suggestions that a person accepts or rejects.
Open the guide (opens in a new tab)The screens, step by step
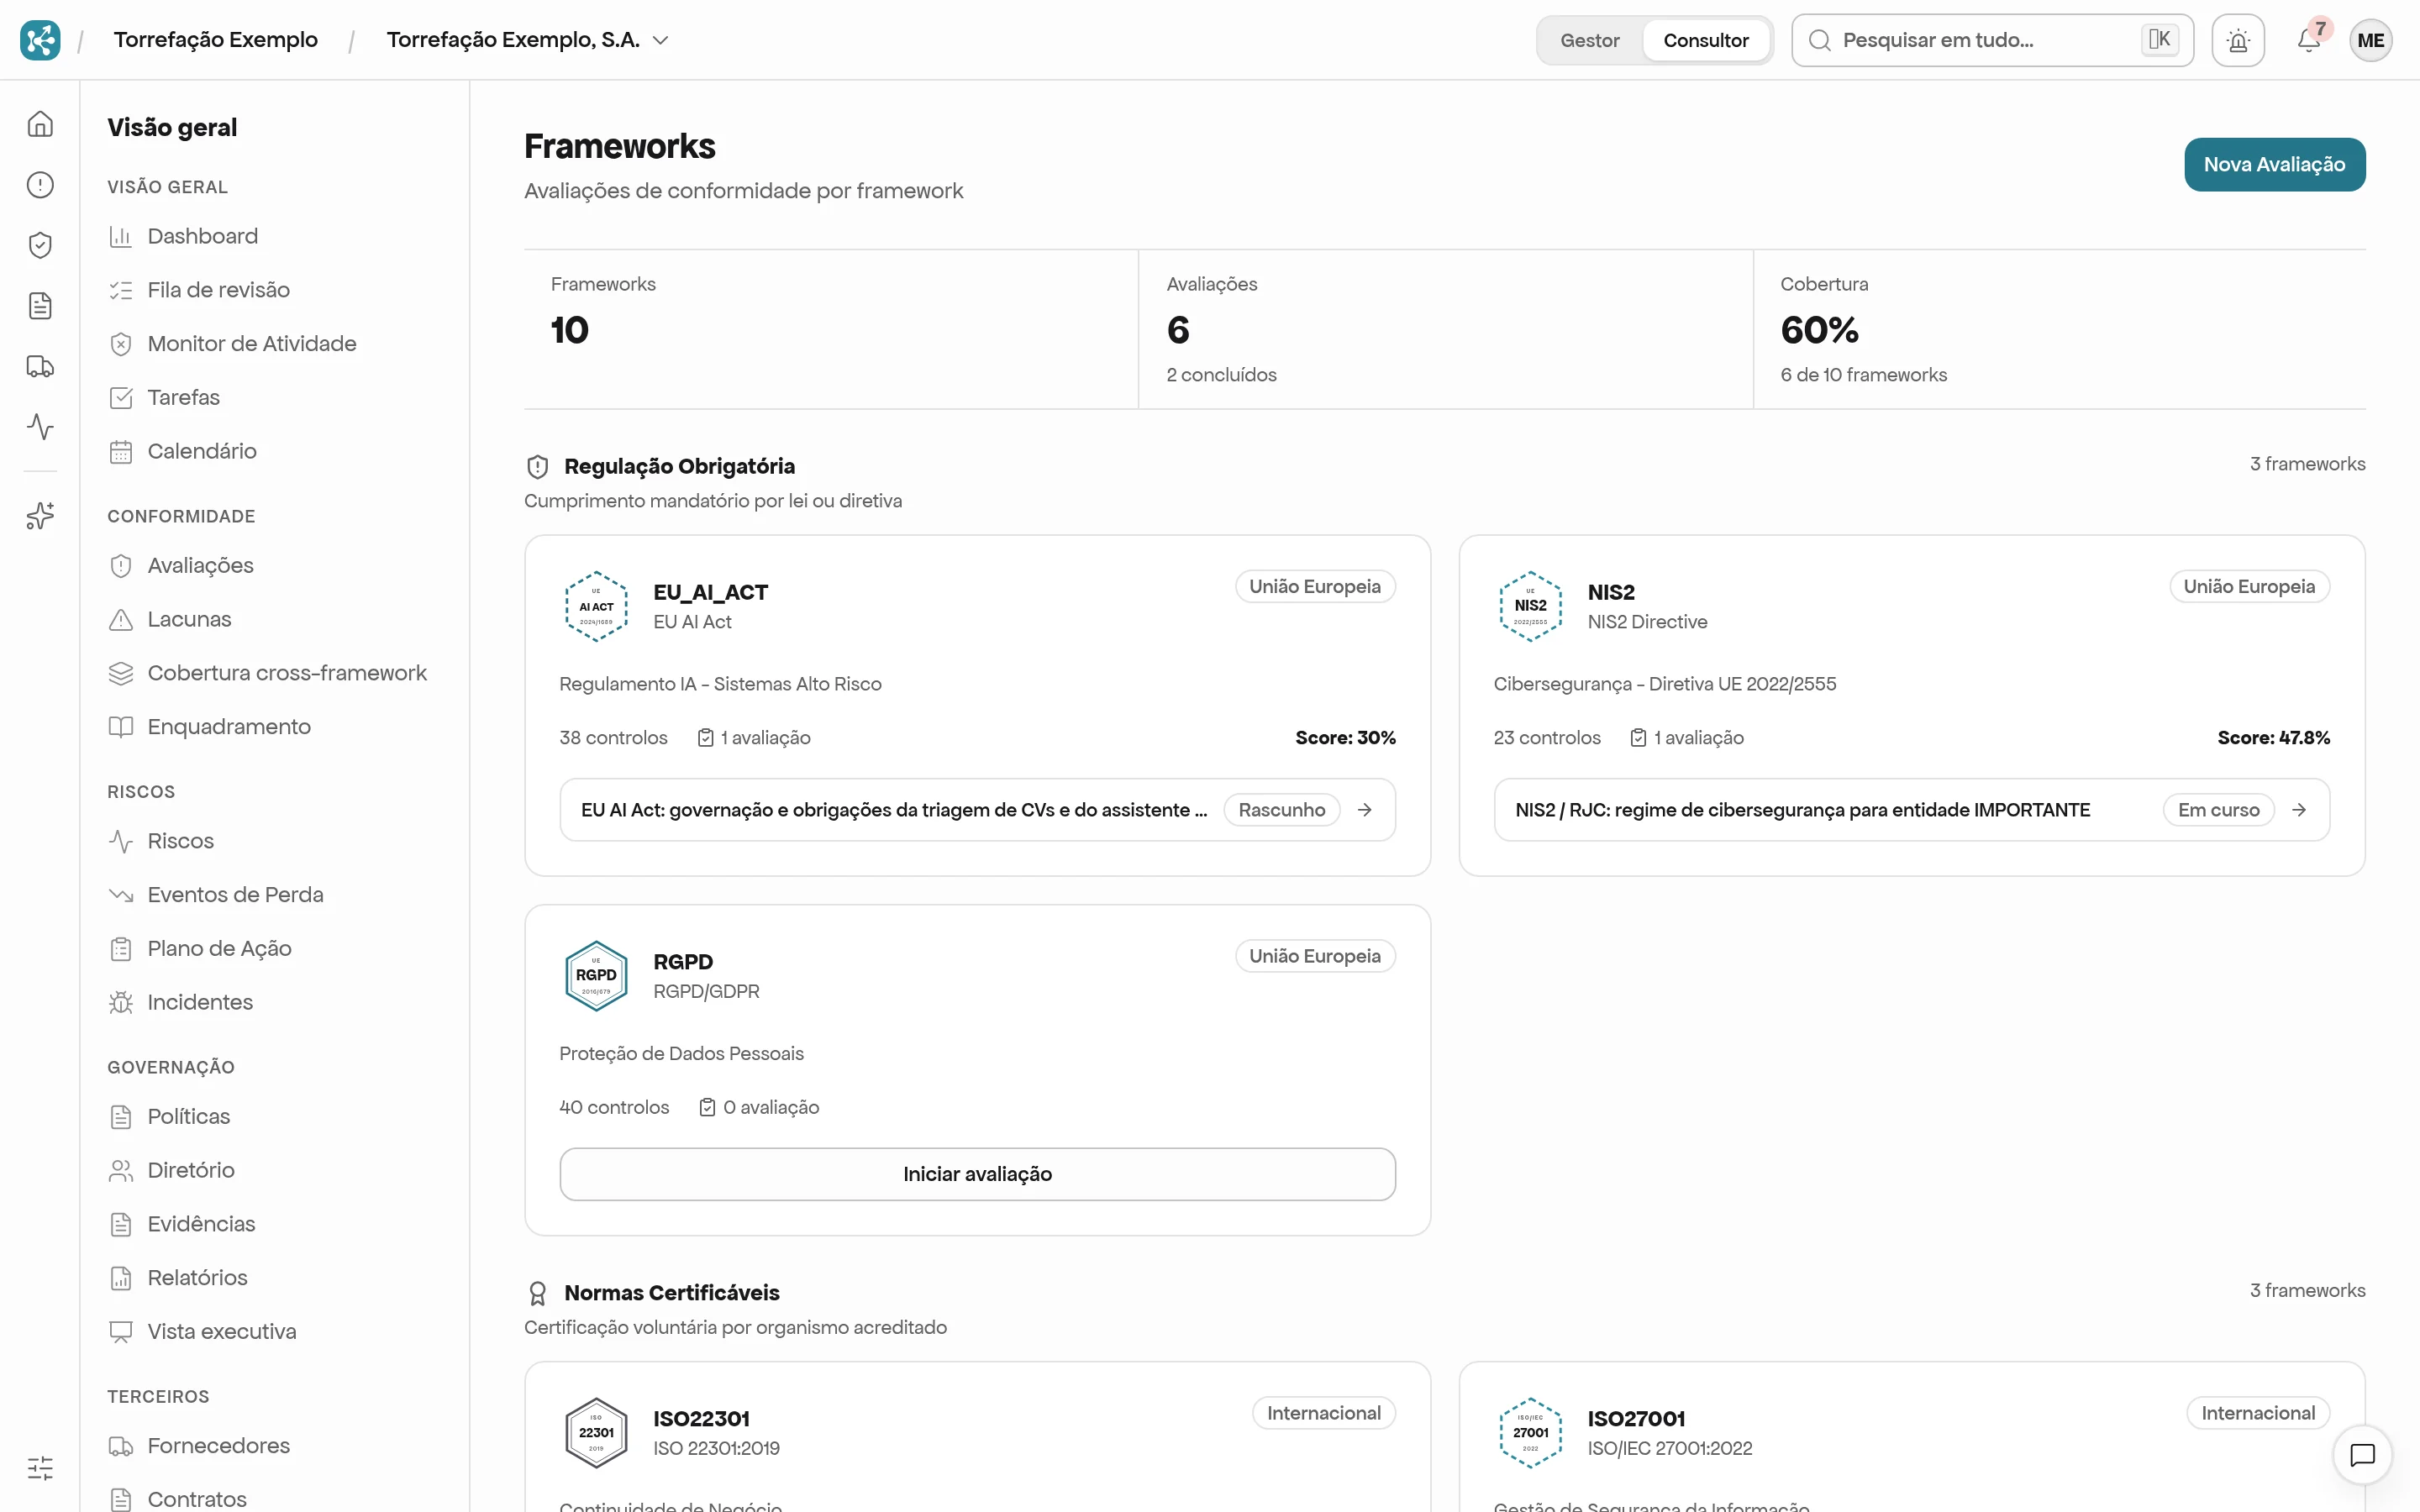
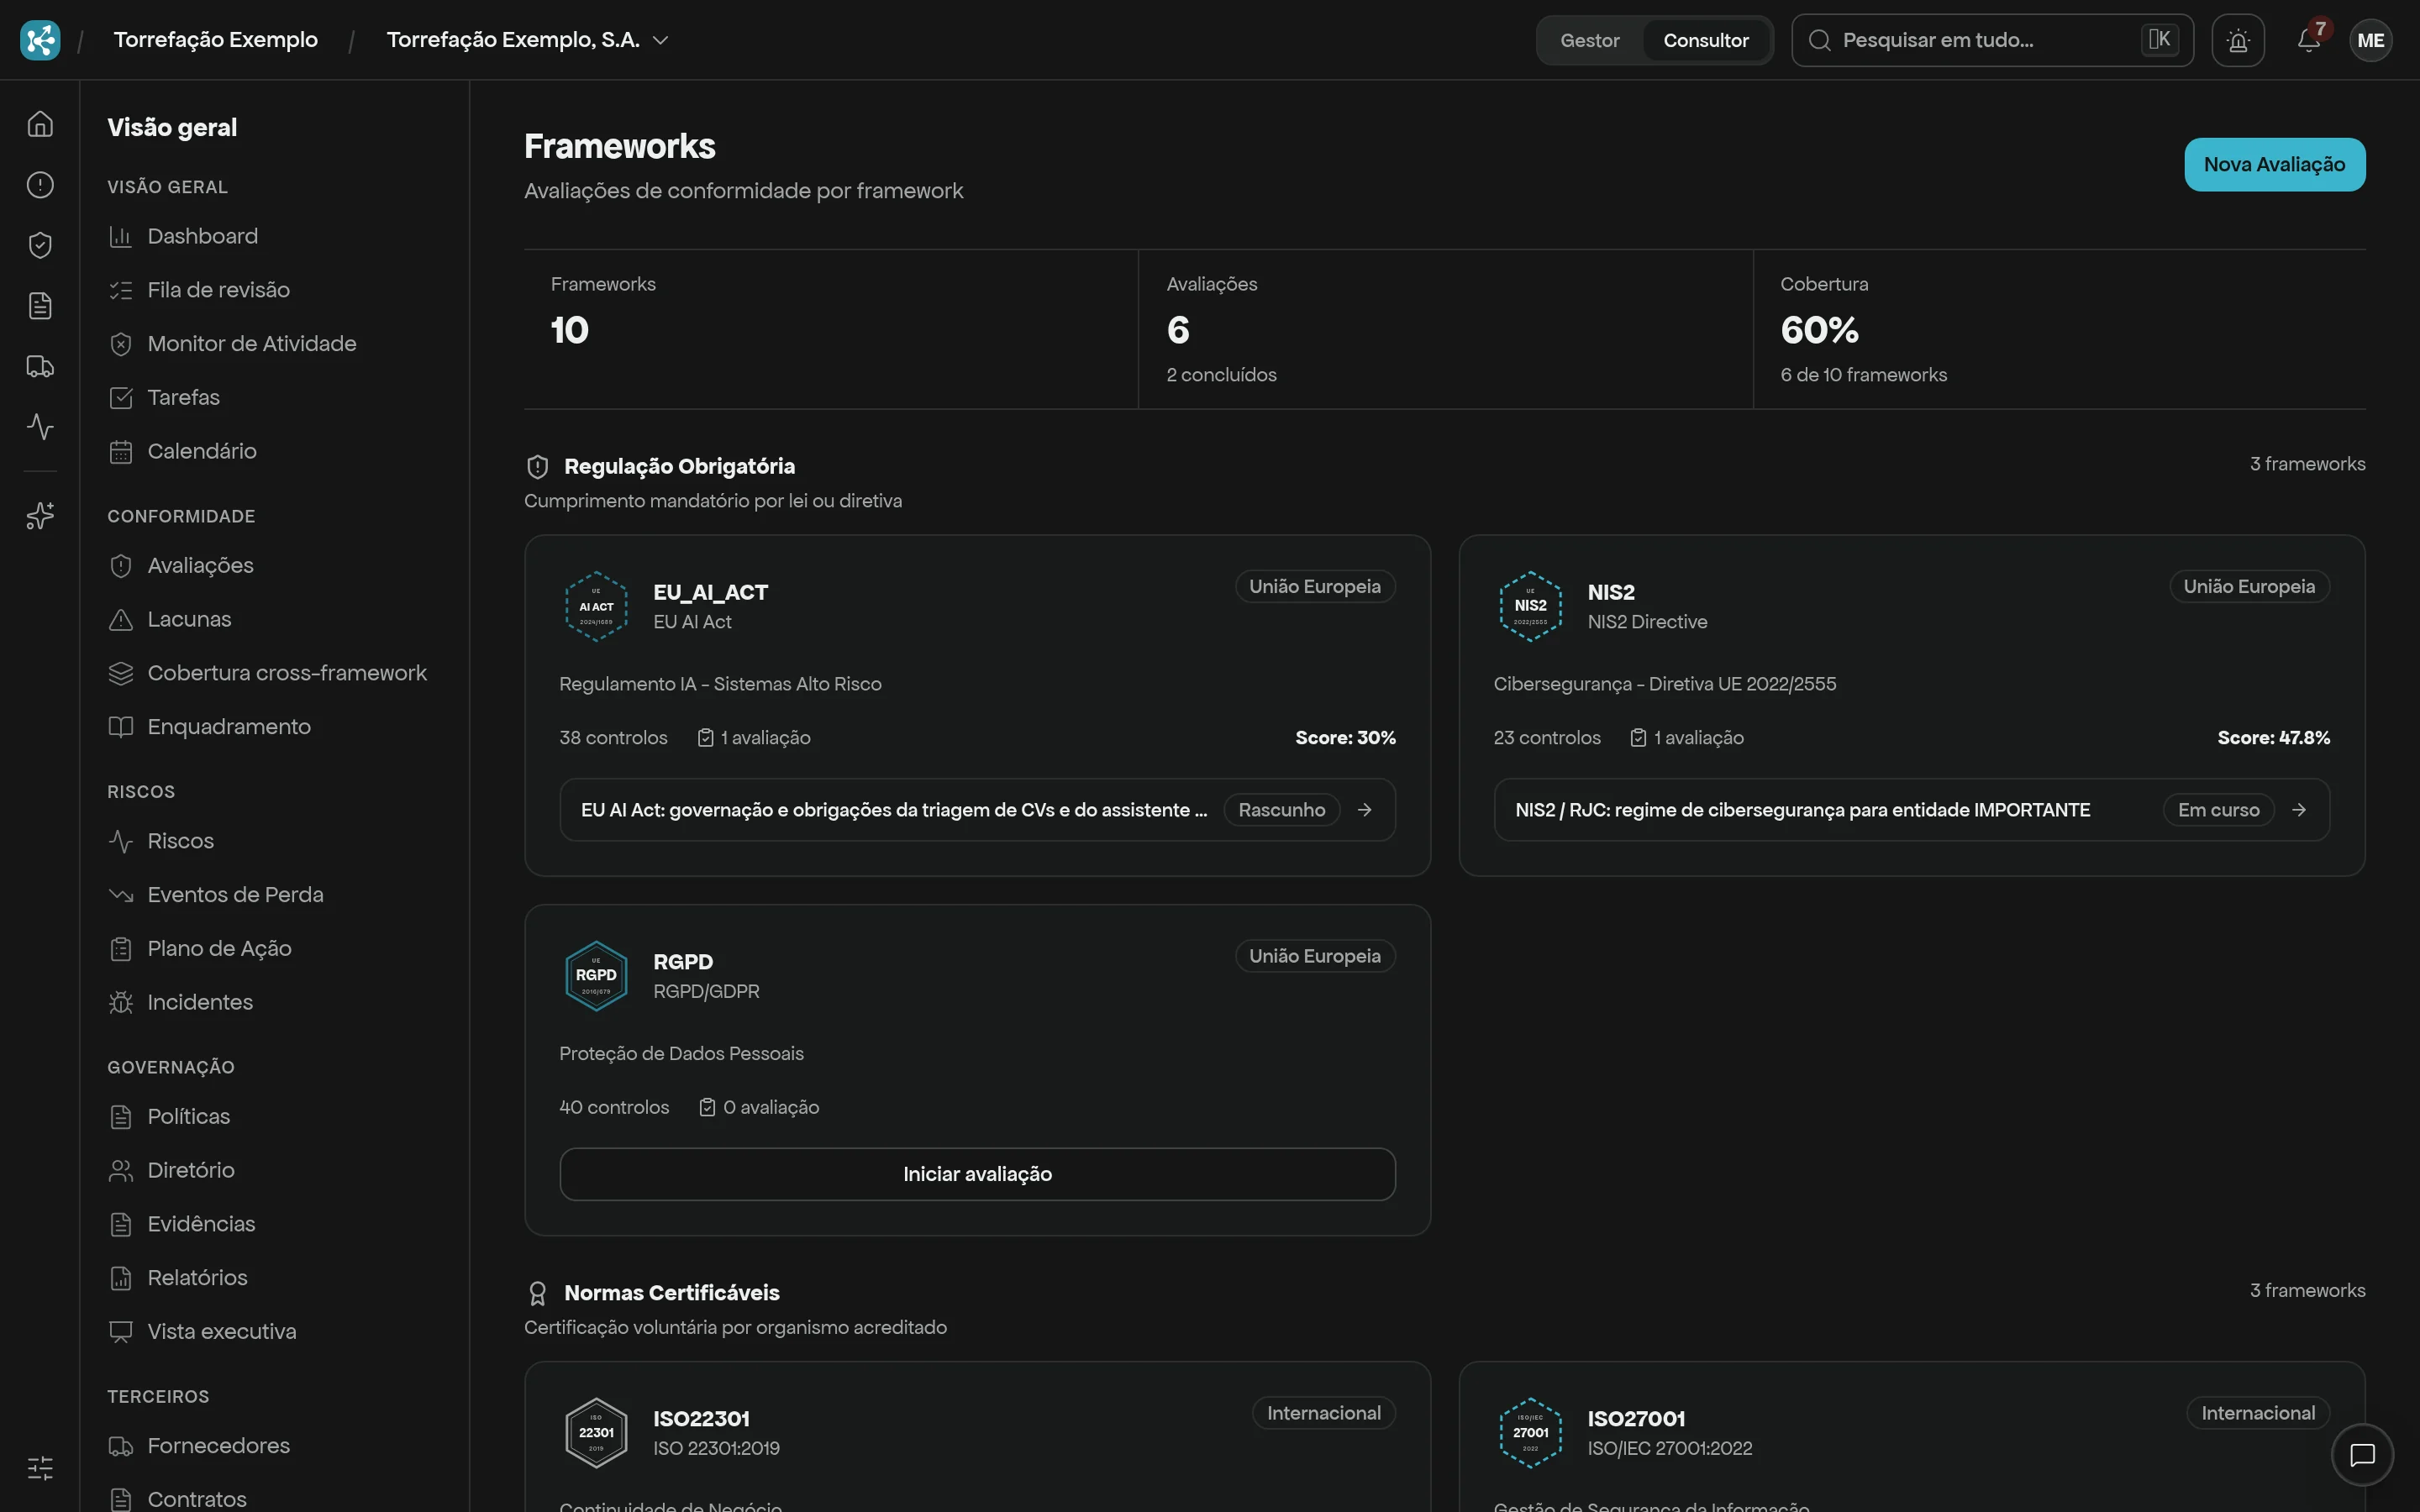
Each framework shows its number of controls, the latest assessment and the score. From here you open the assessment and the status of each control.
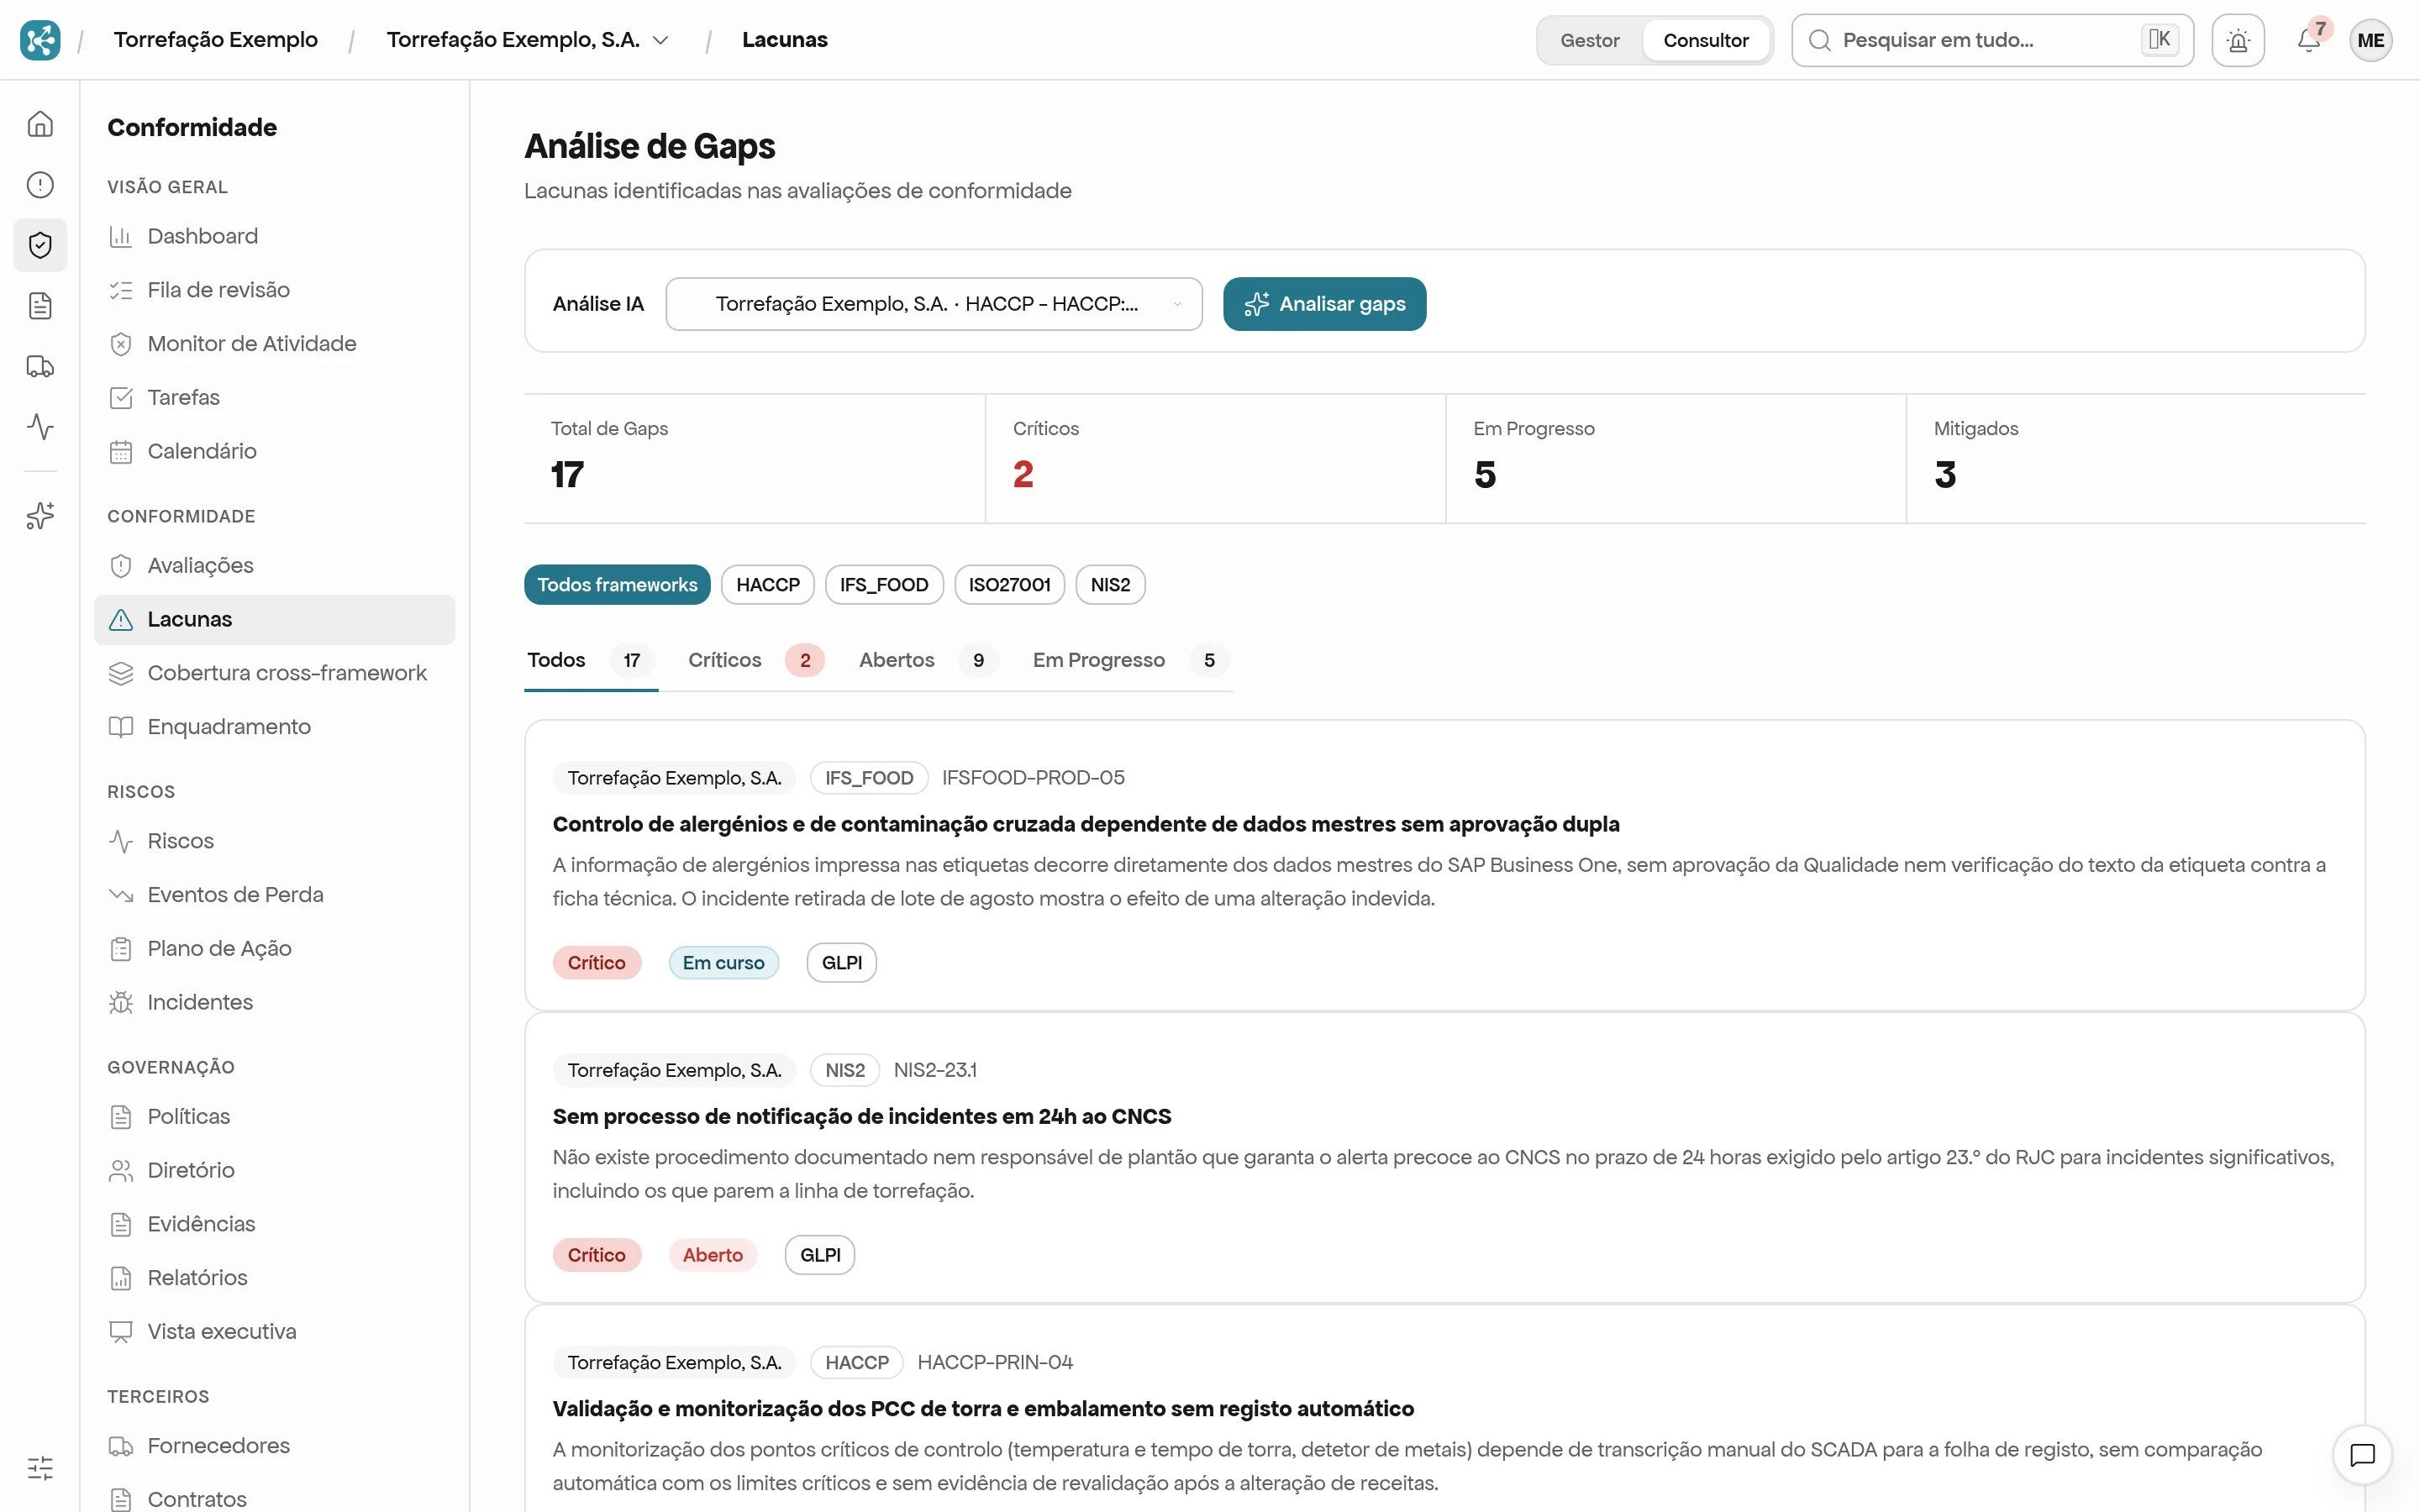
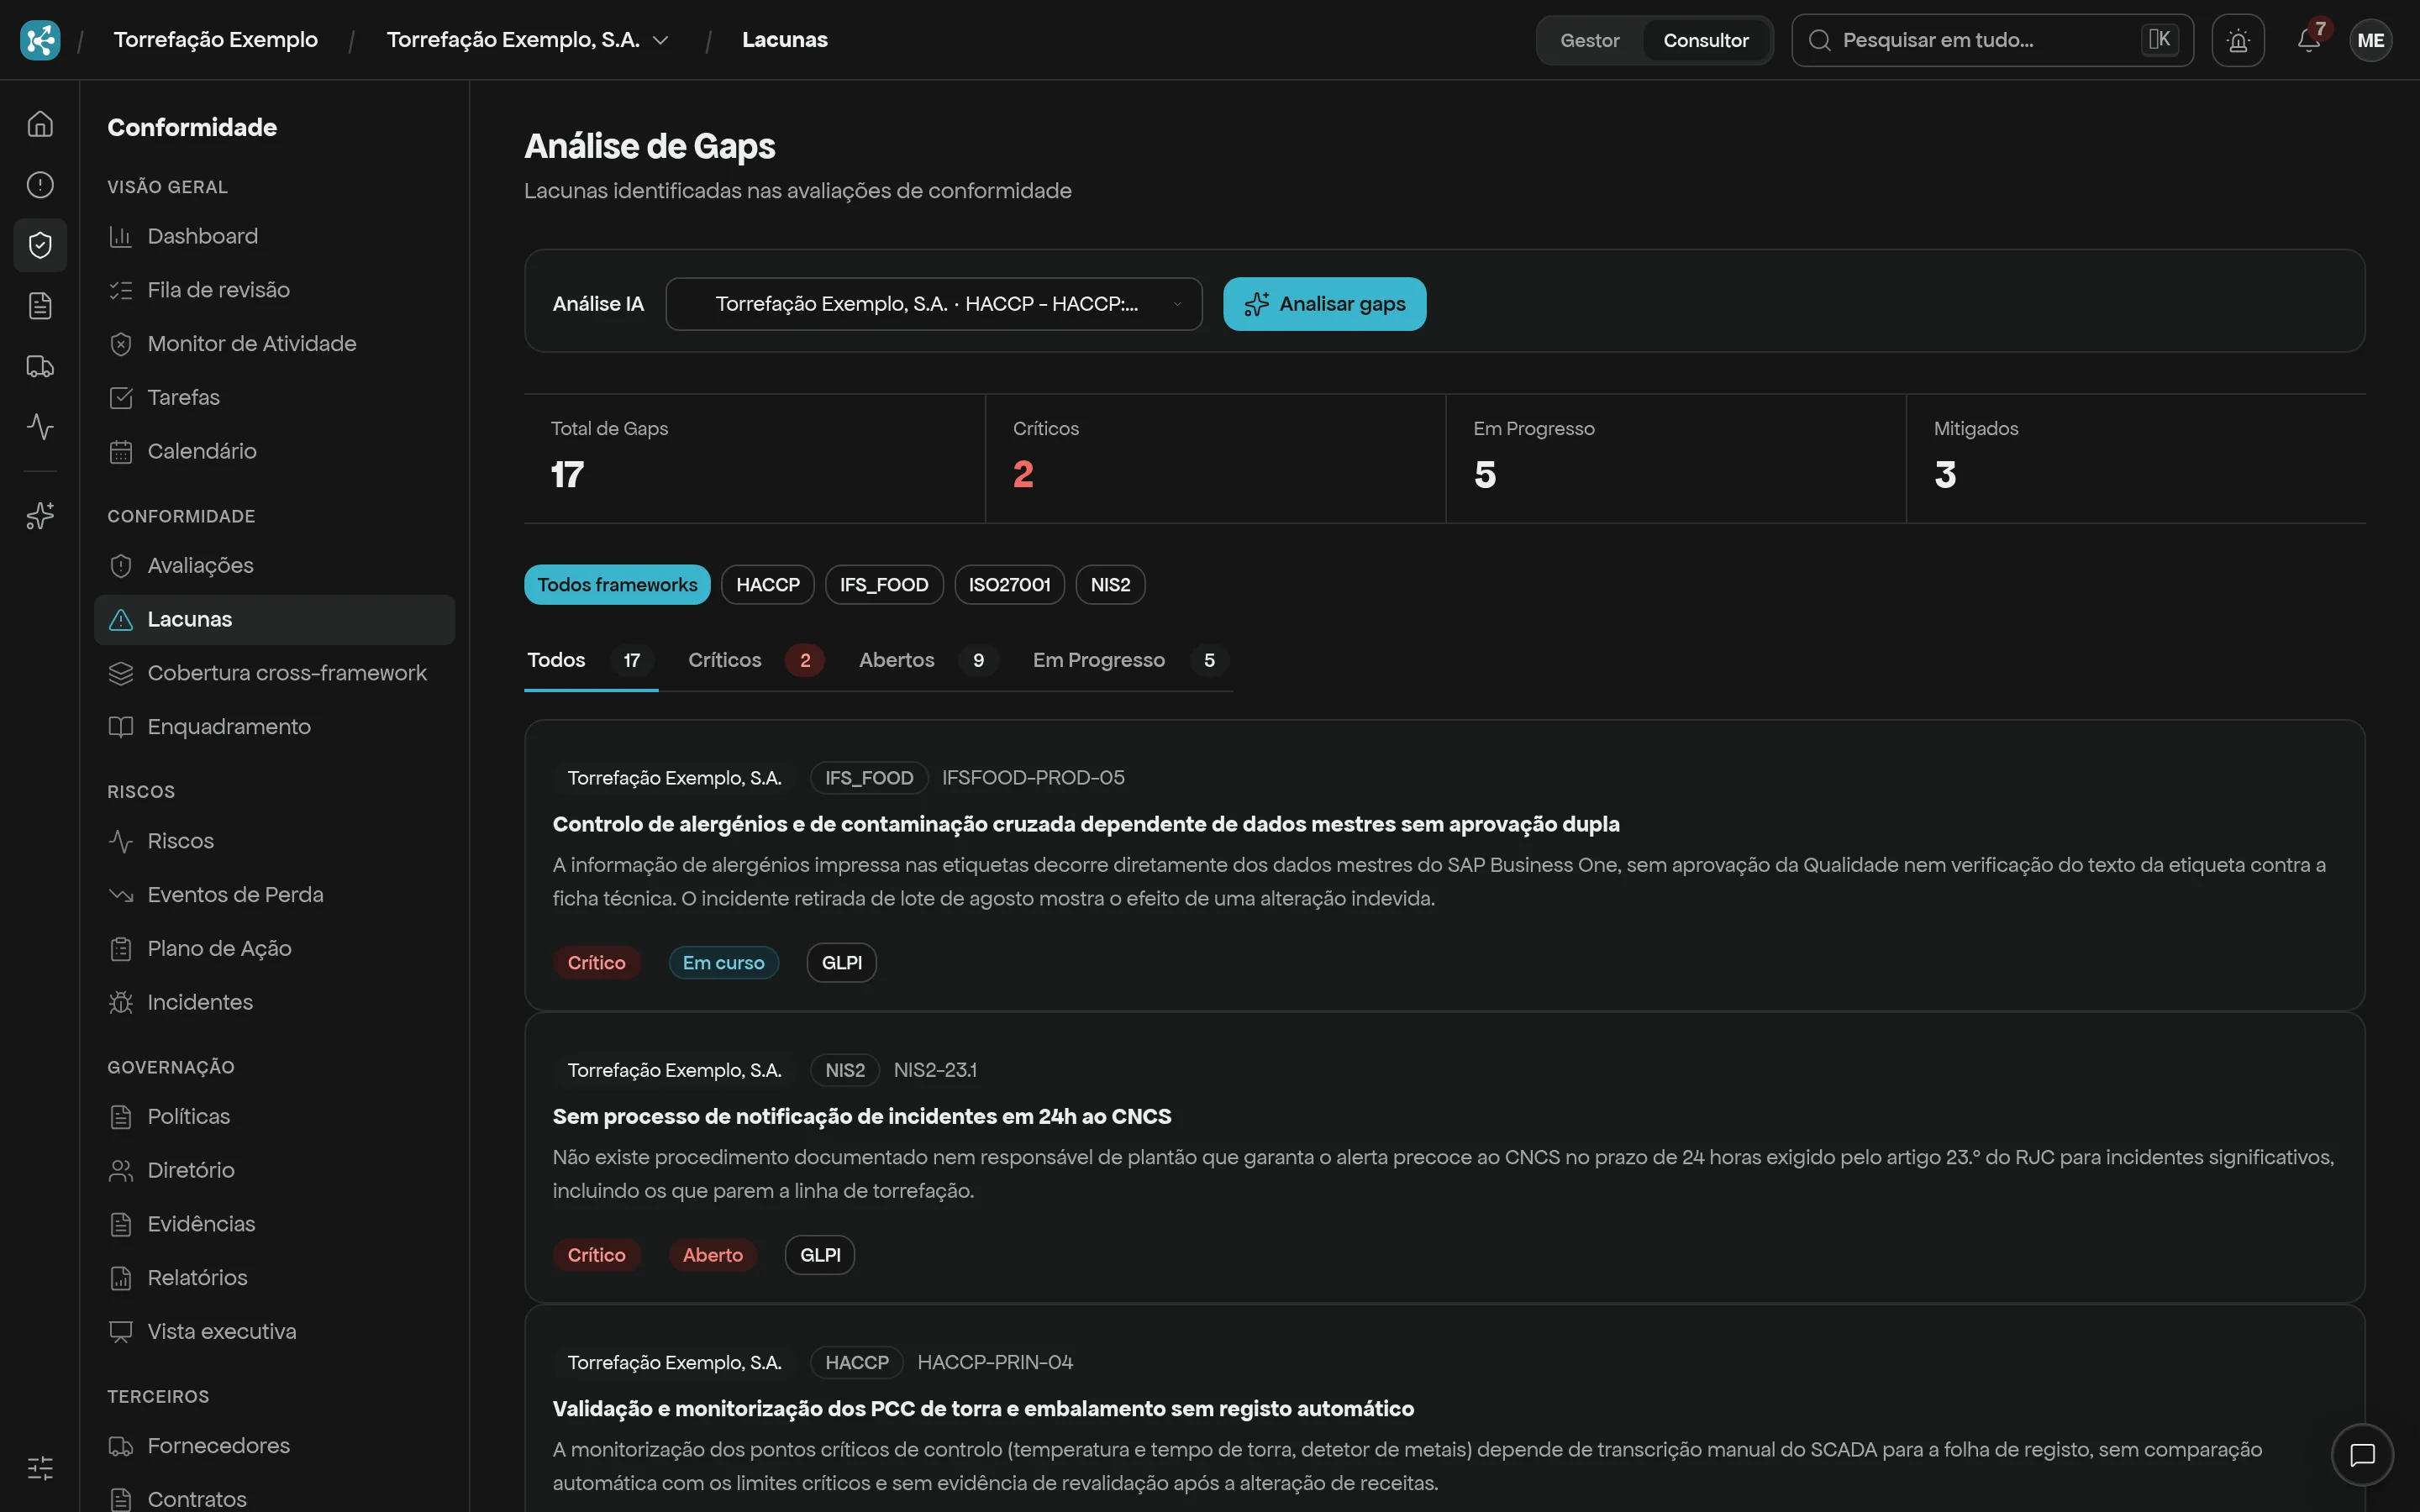
The gaps found in assessments, with severity and status. Filter by framework and by priority, and see what is open, in progress or mitigated.
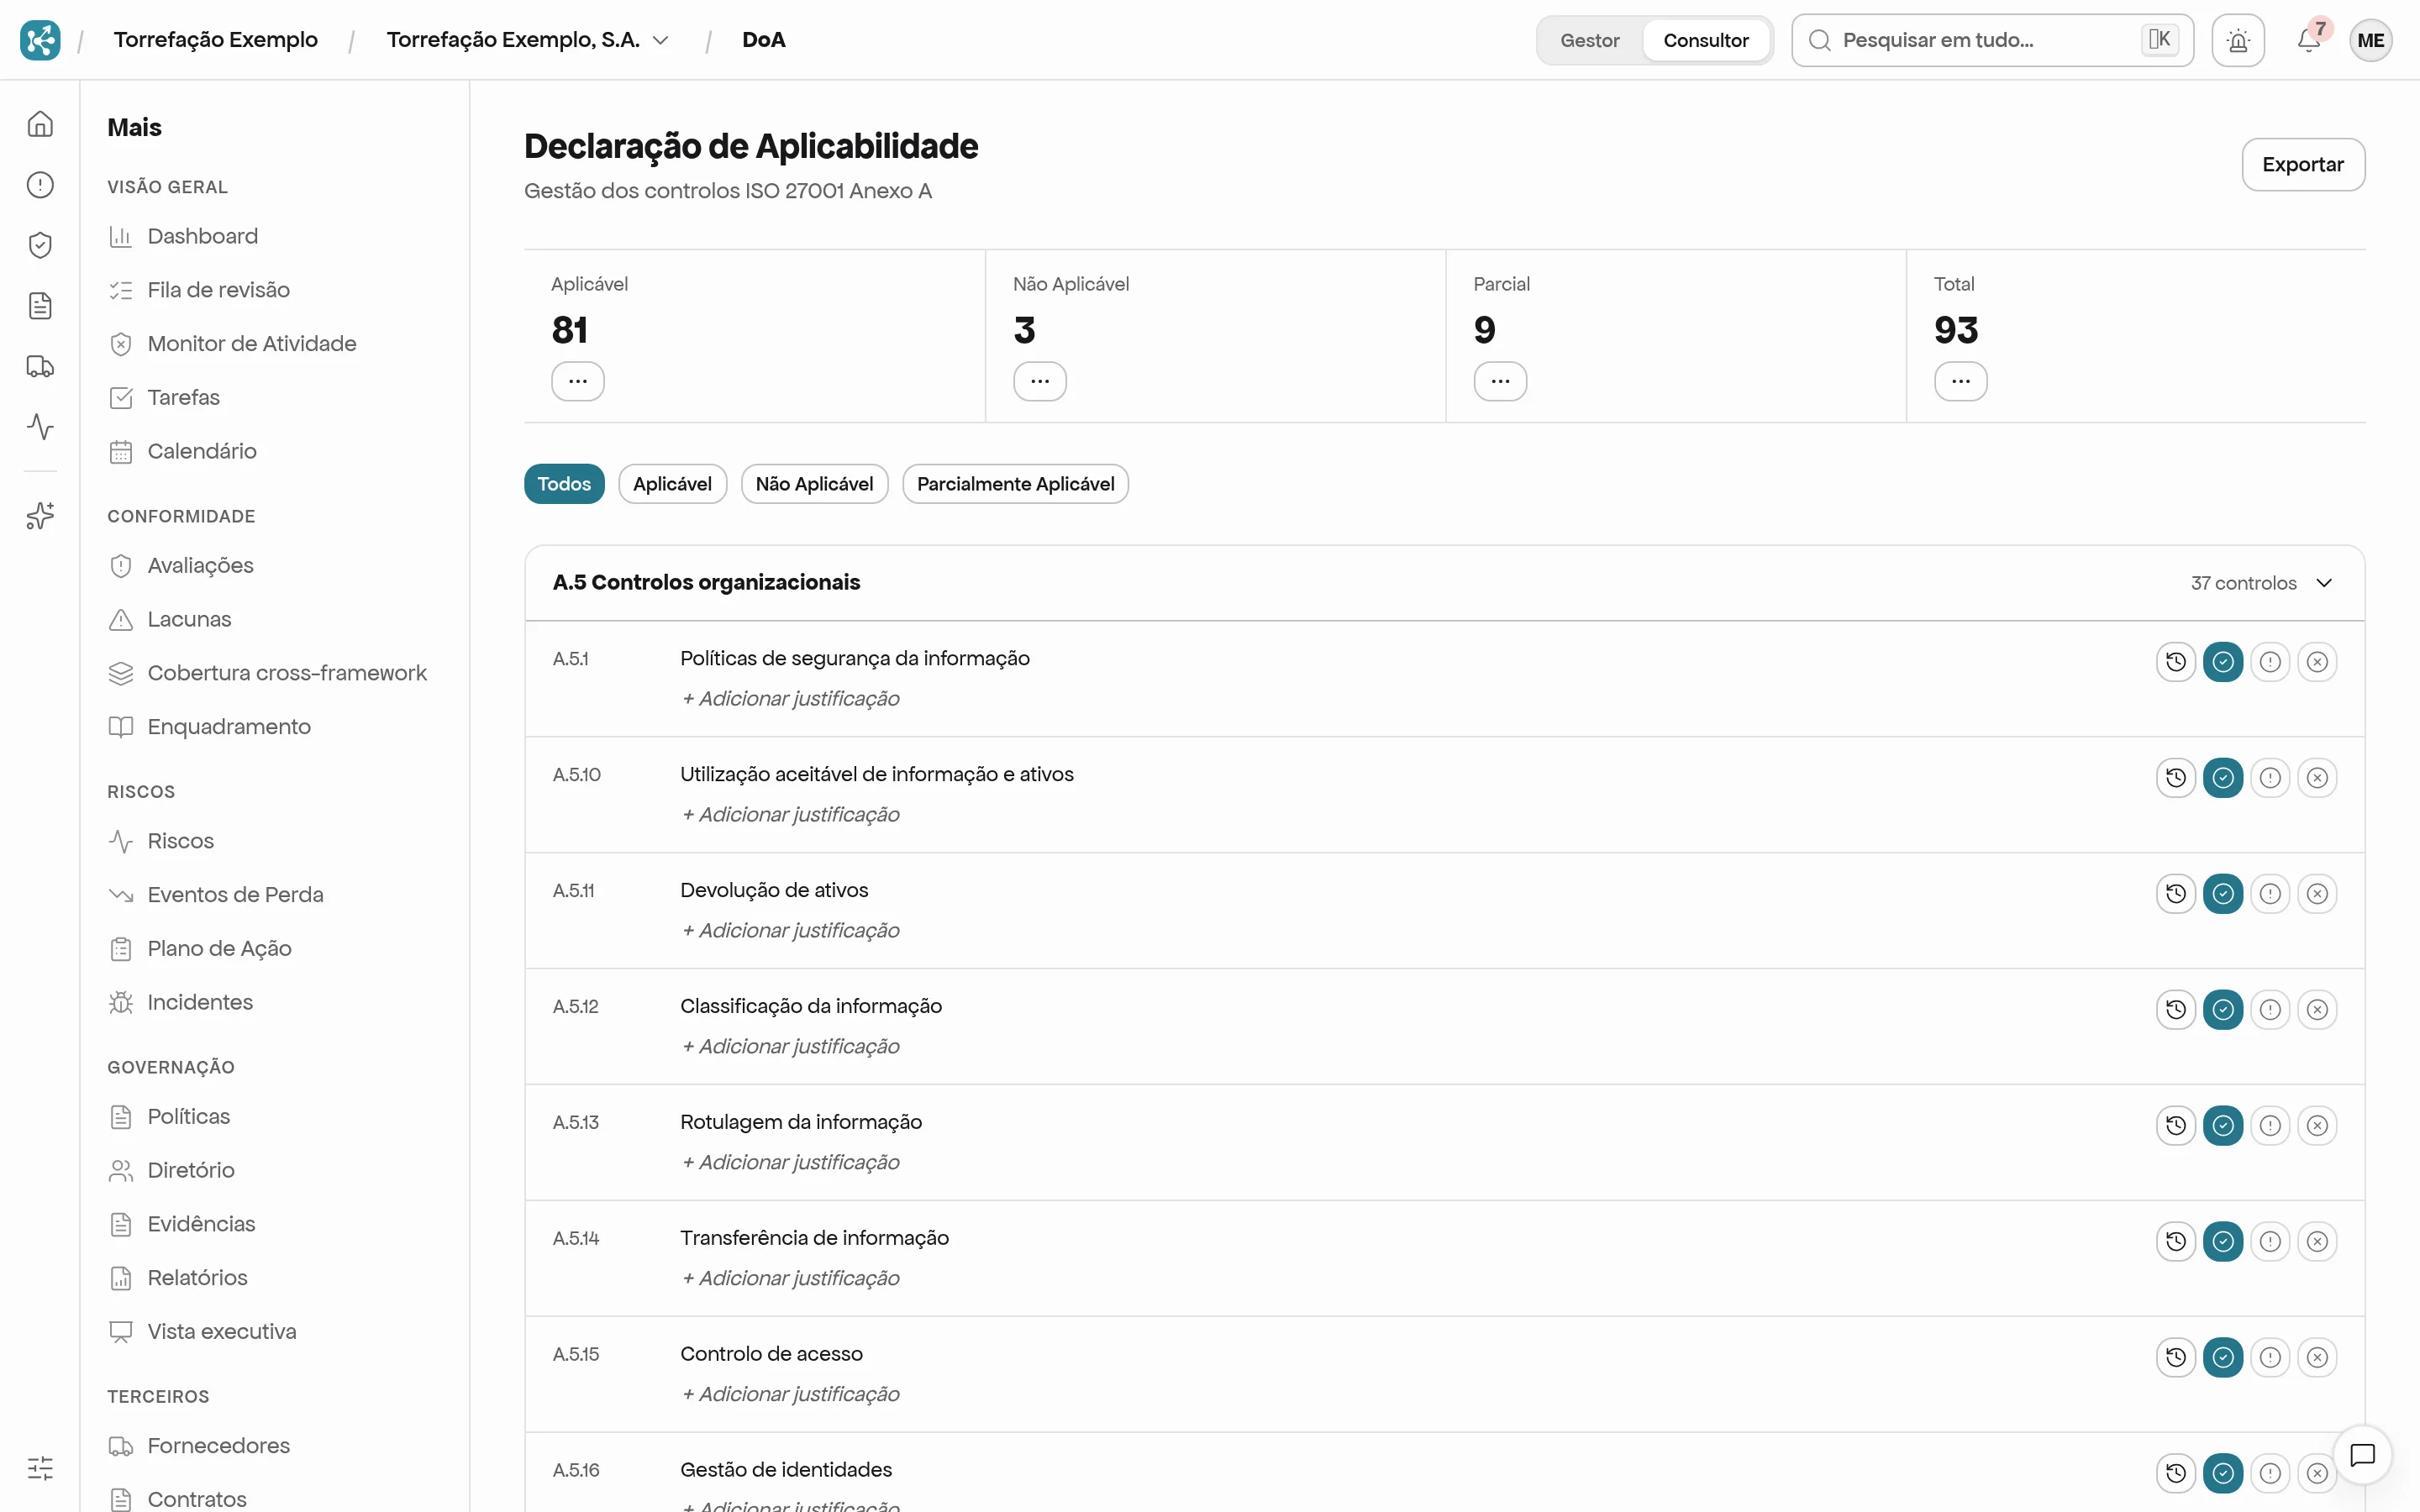
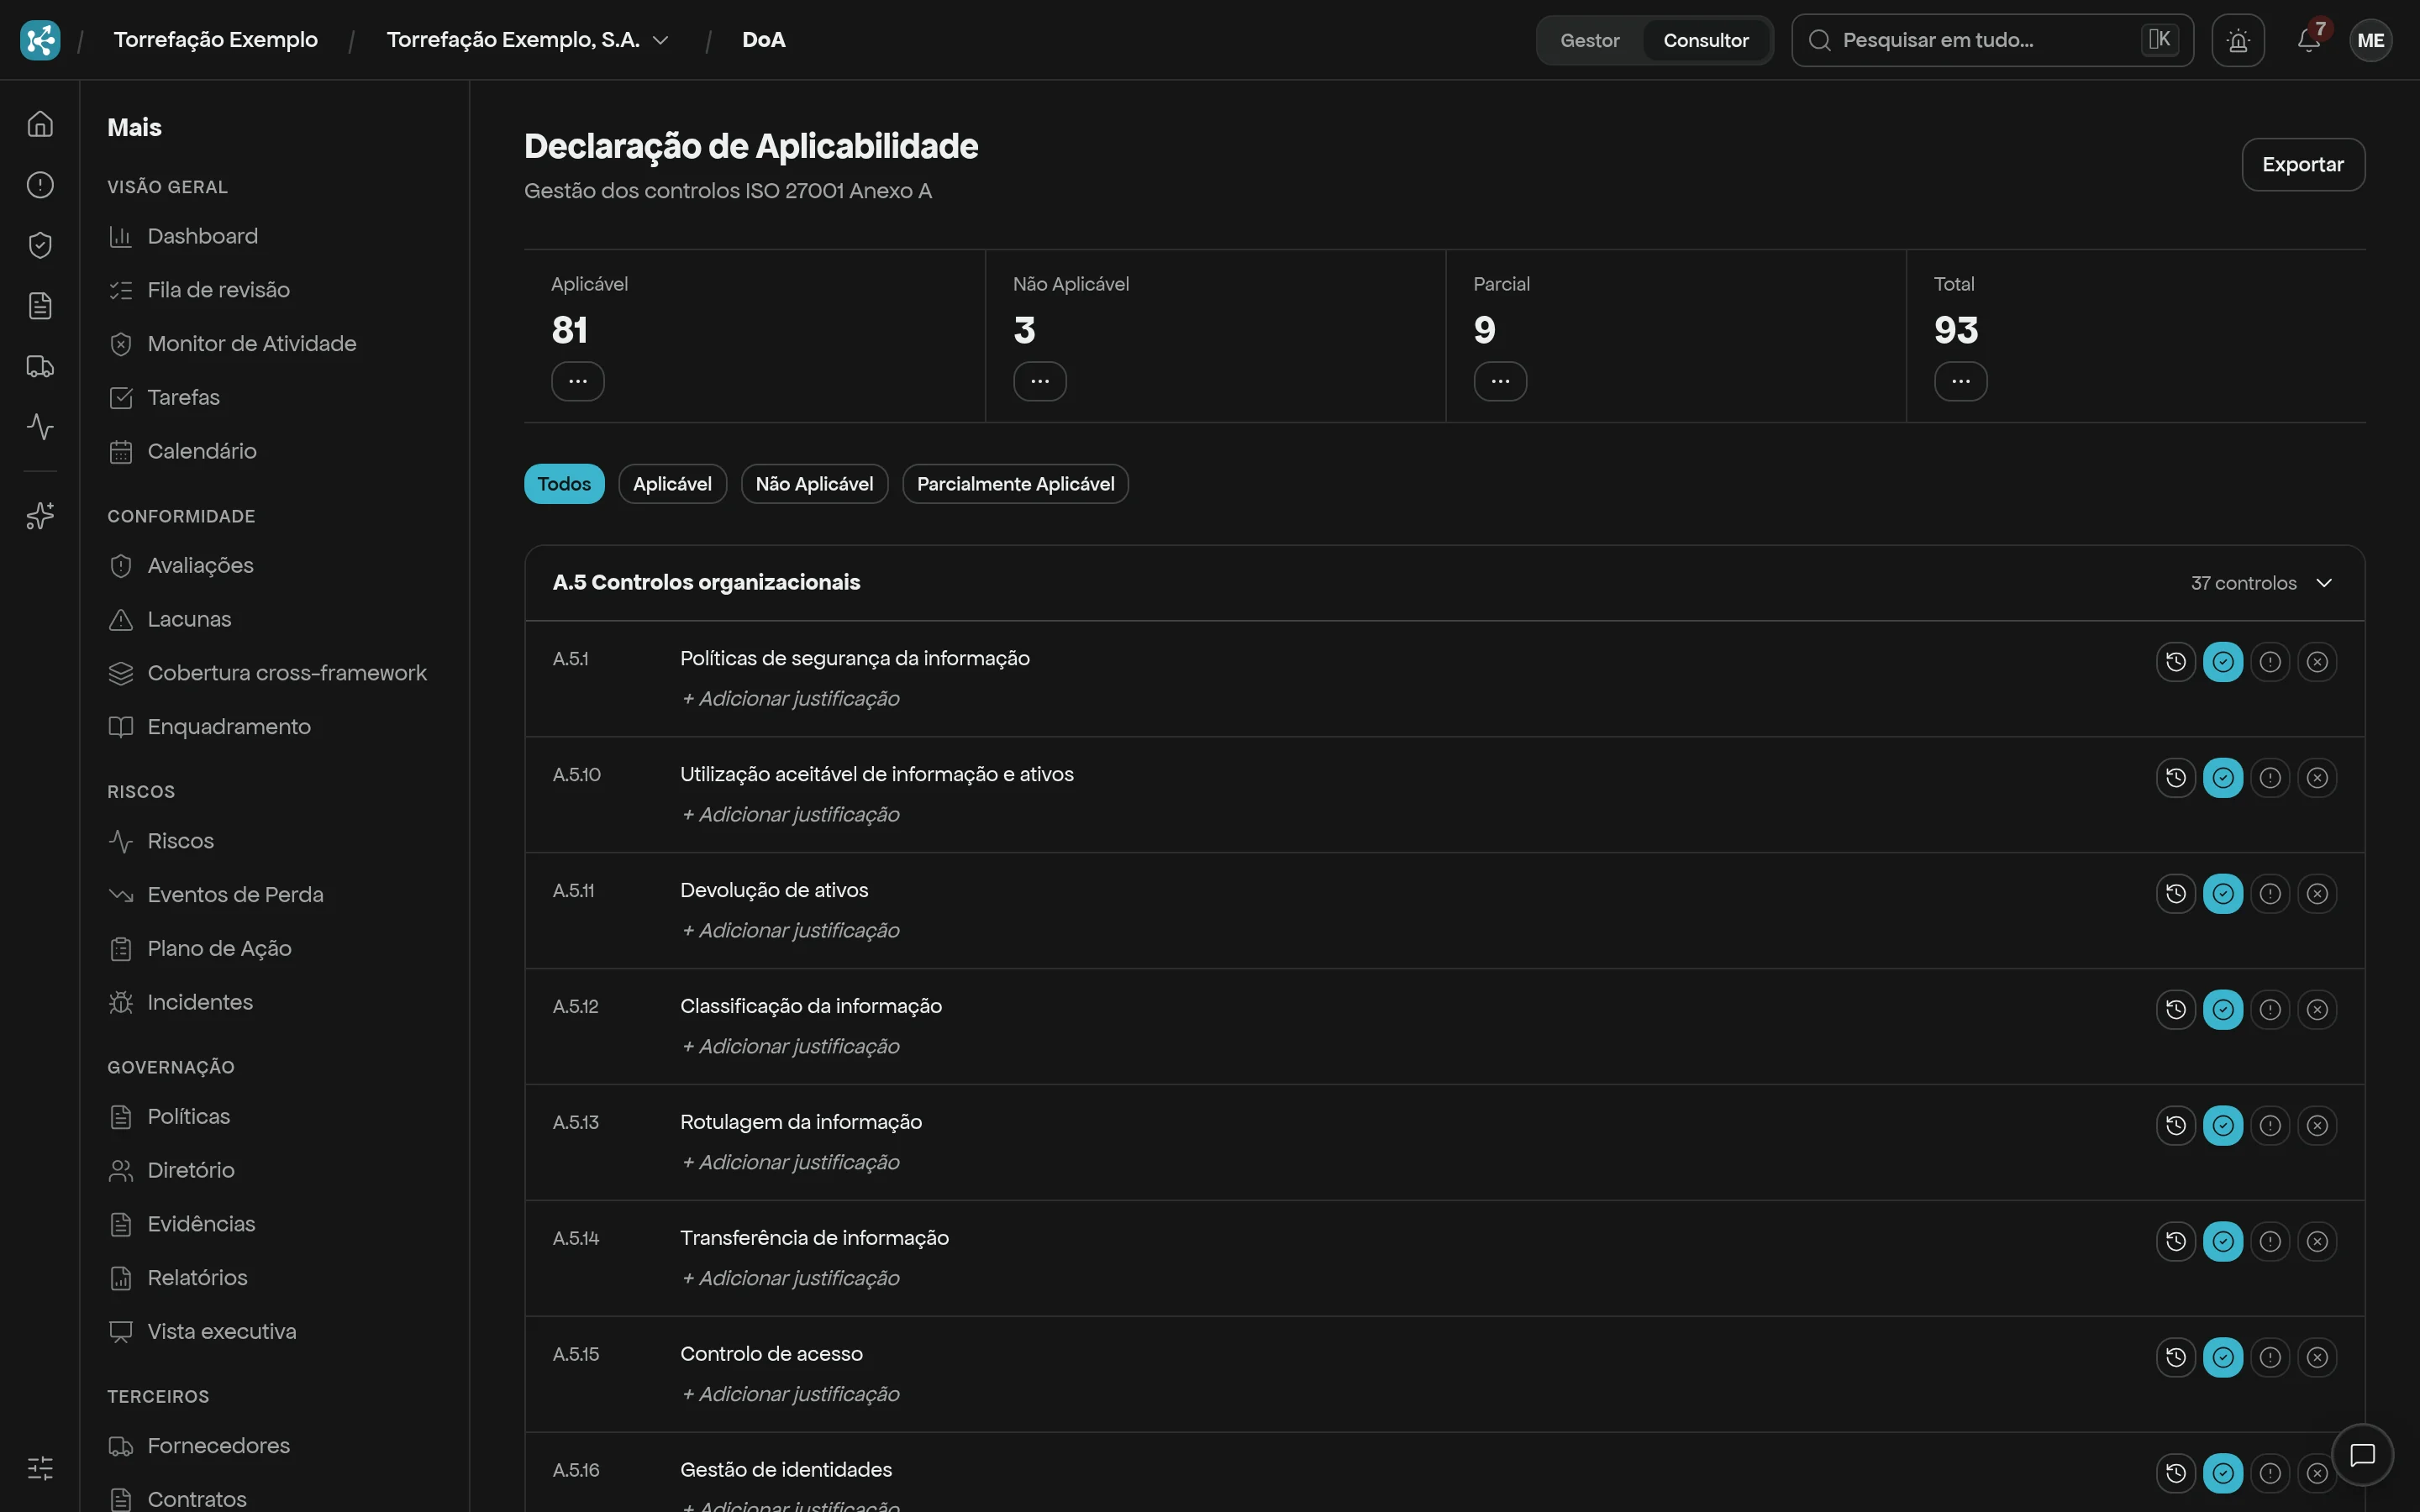
Each ISO 27001 Annex A control is marked applicable, not applicable or partial, with its status and room for the justification.
In the documentation
The user guide explains this module step by step.