Frameworks
NIS2 in Portugal: what it asks for and how to comply
NIS2 is the European directive on the security of network and information systems. It asks covered organizations for cybersecurity risk management measures, with management accountability, and for incident notification. In EterShield, the controls cover articles 20 to 23.
Reference: Directive (EU) 2022/2555 · 23 controls
Highlights
- Governance and management accountability (Art. 20): management approves the measures and oversees their implementation.
- Security measures (Art. 21): risk analysis, policies, incident handling and business continuity.
- Incident notification (Art. 23) and controls by category, each with its own priority.
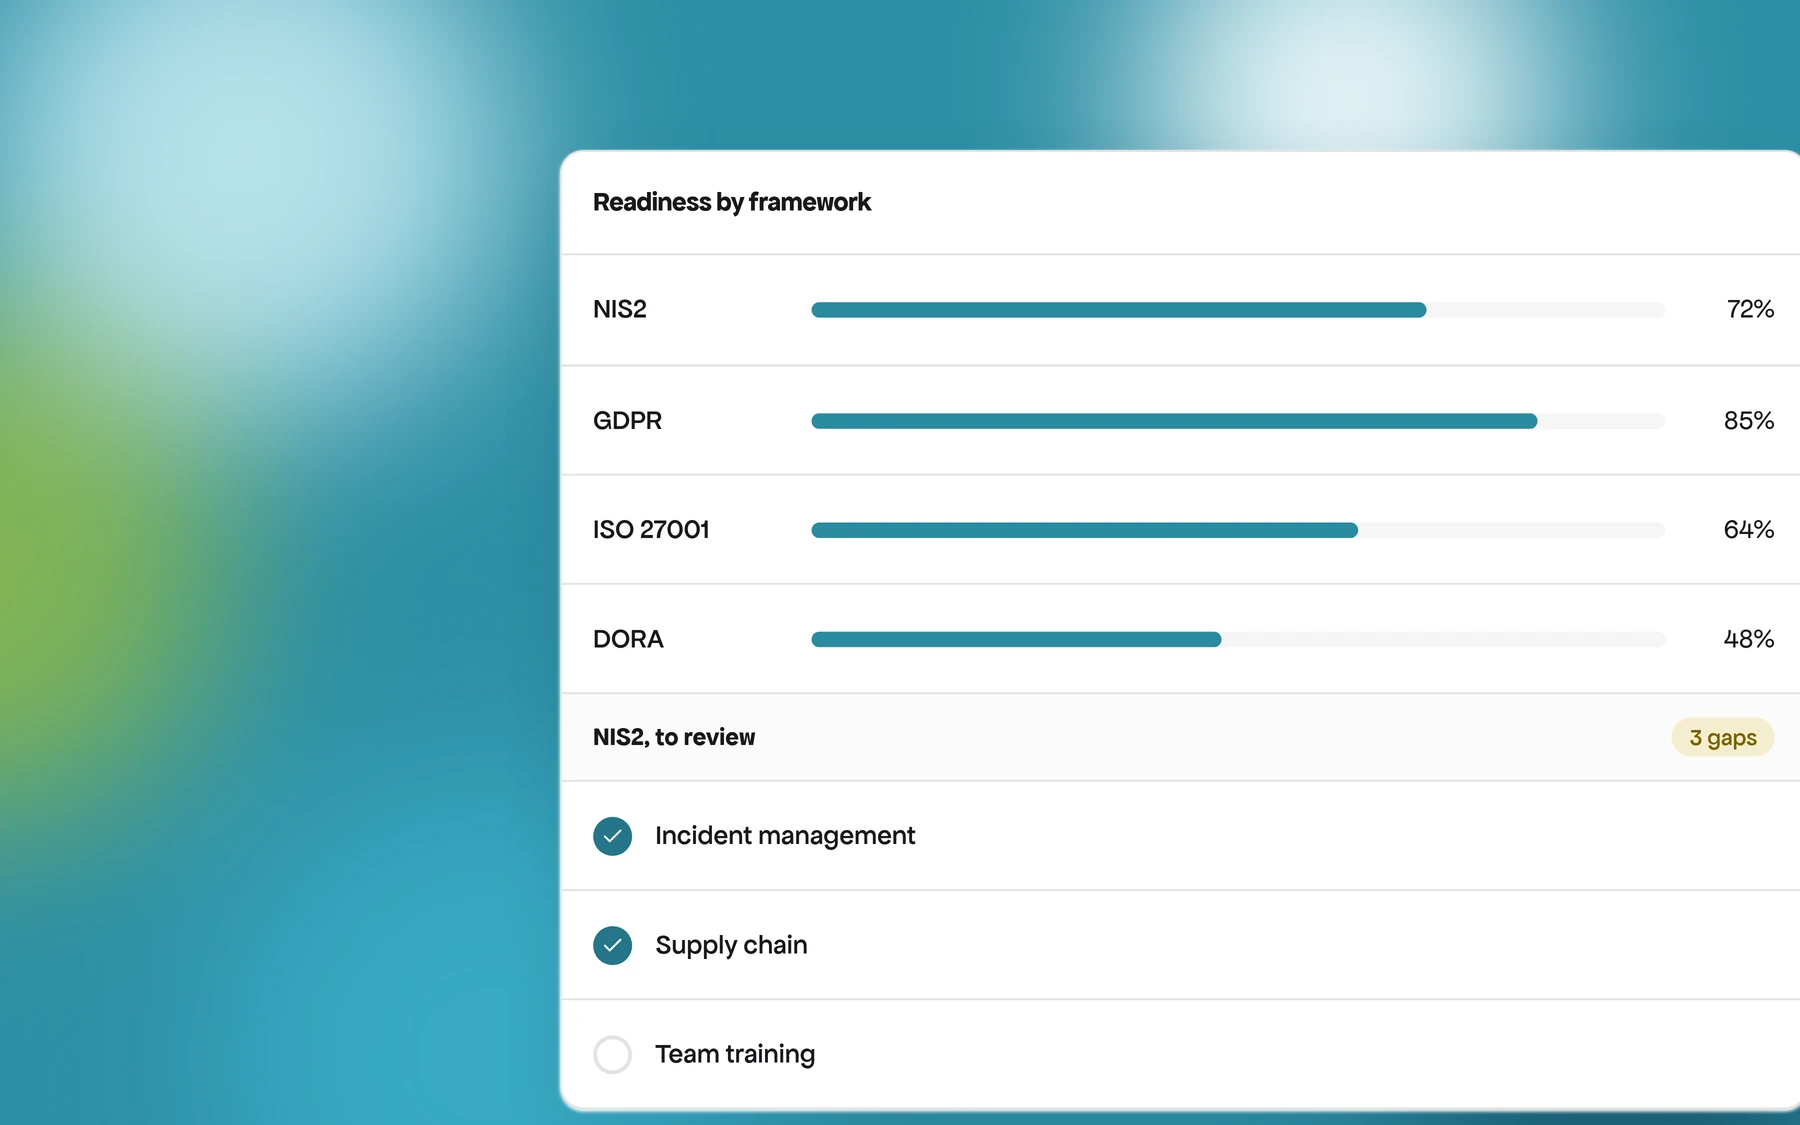
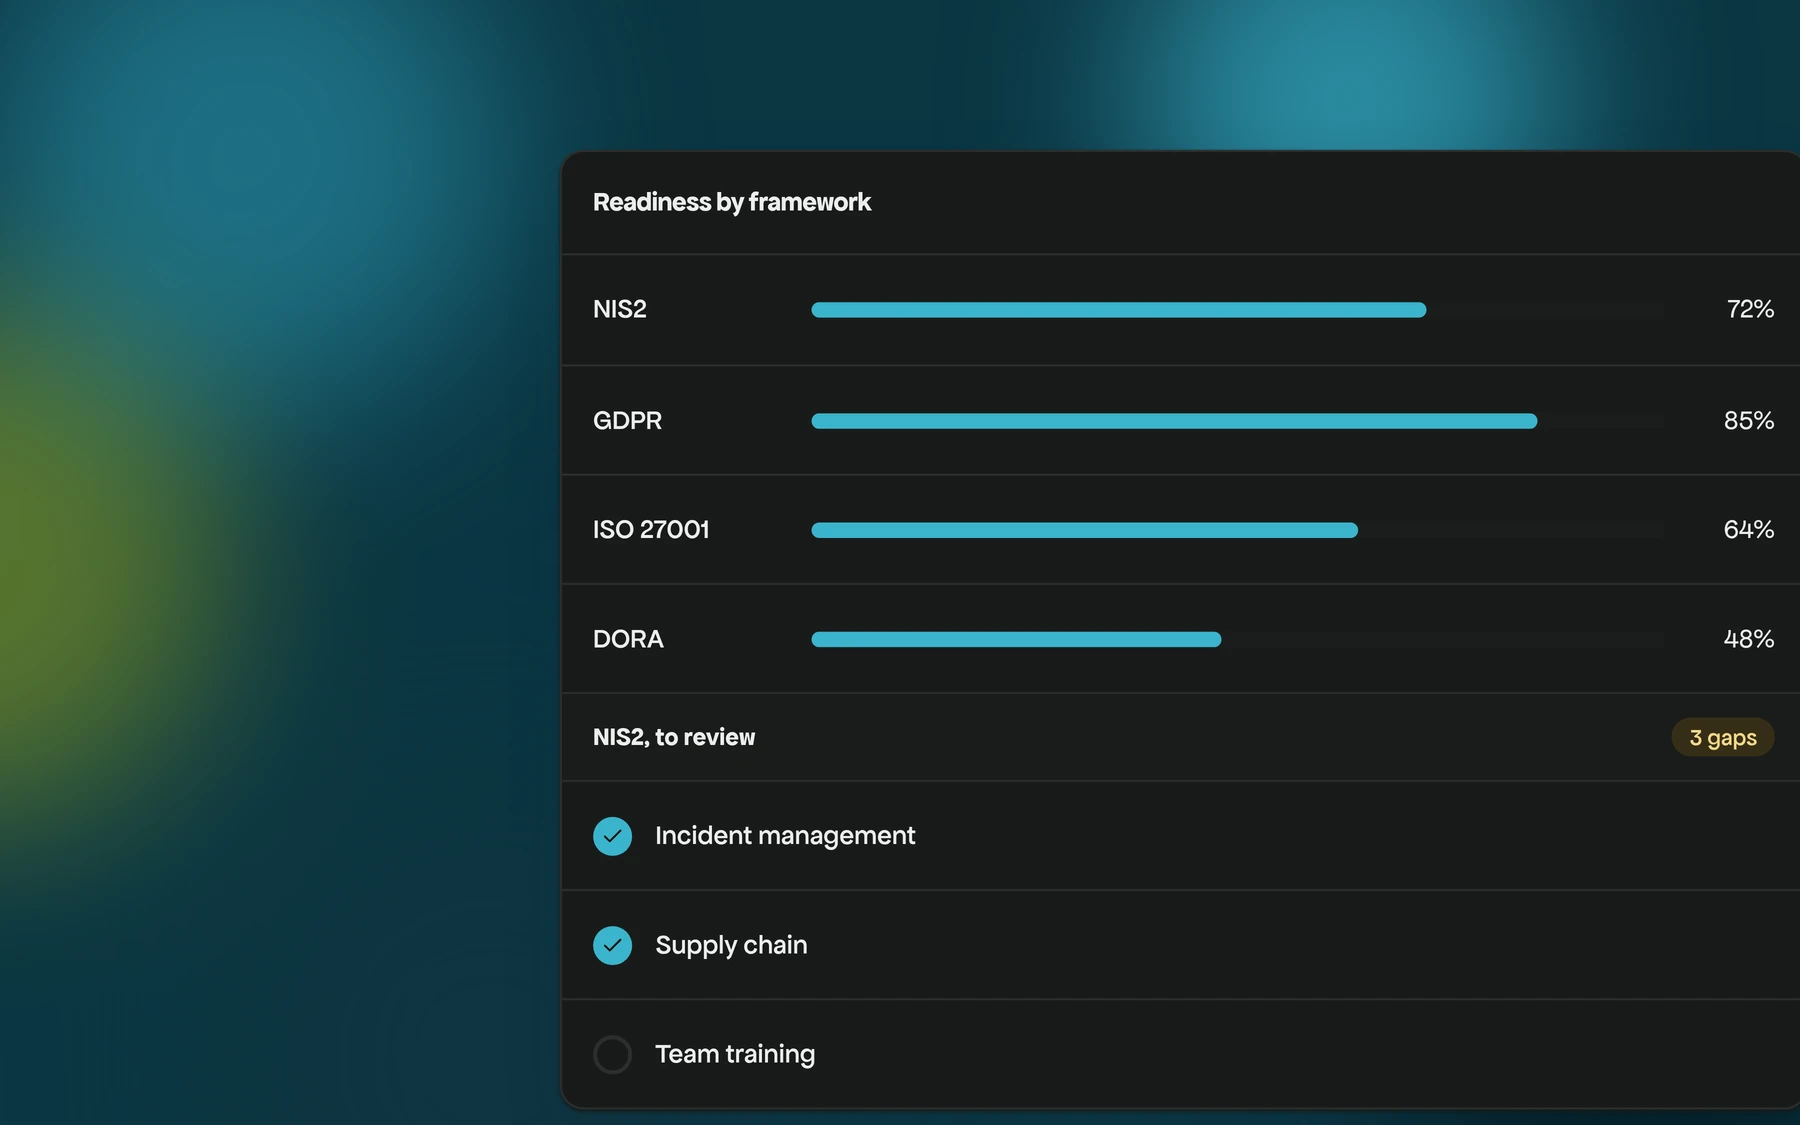
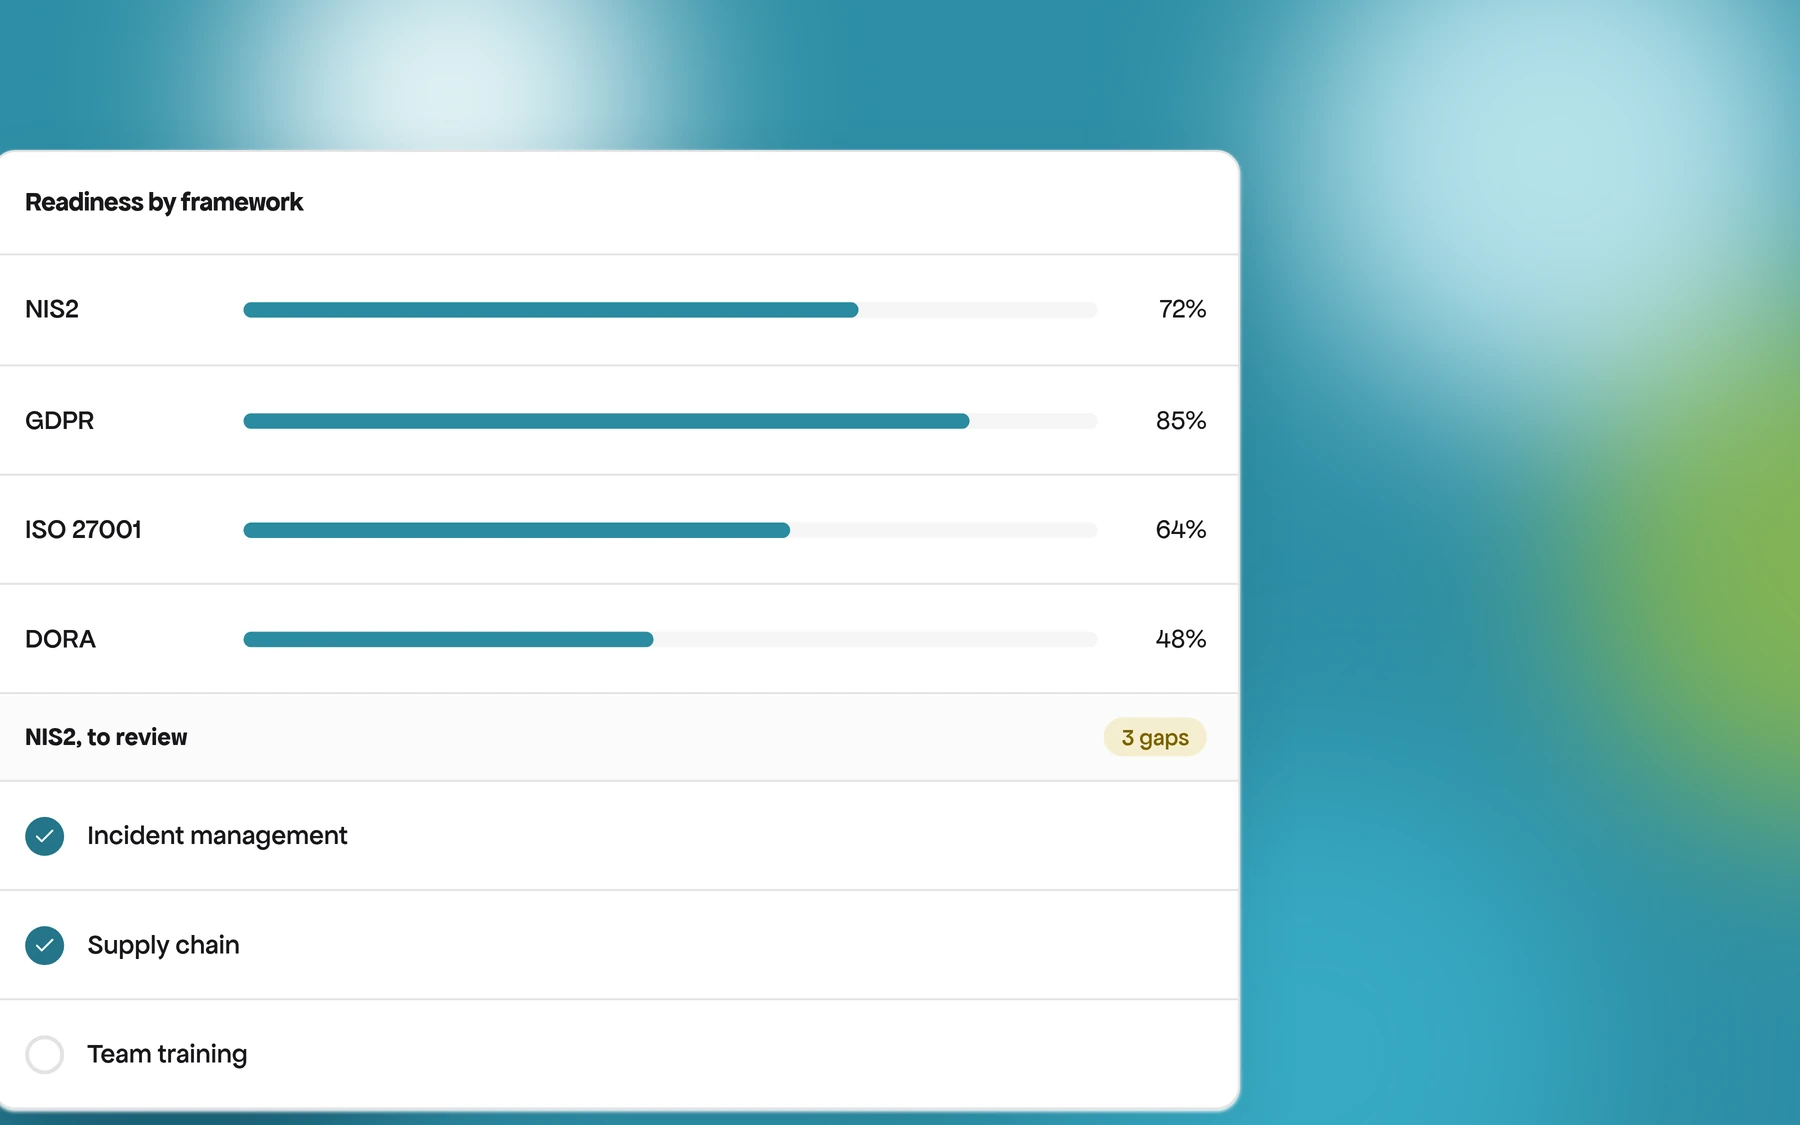
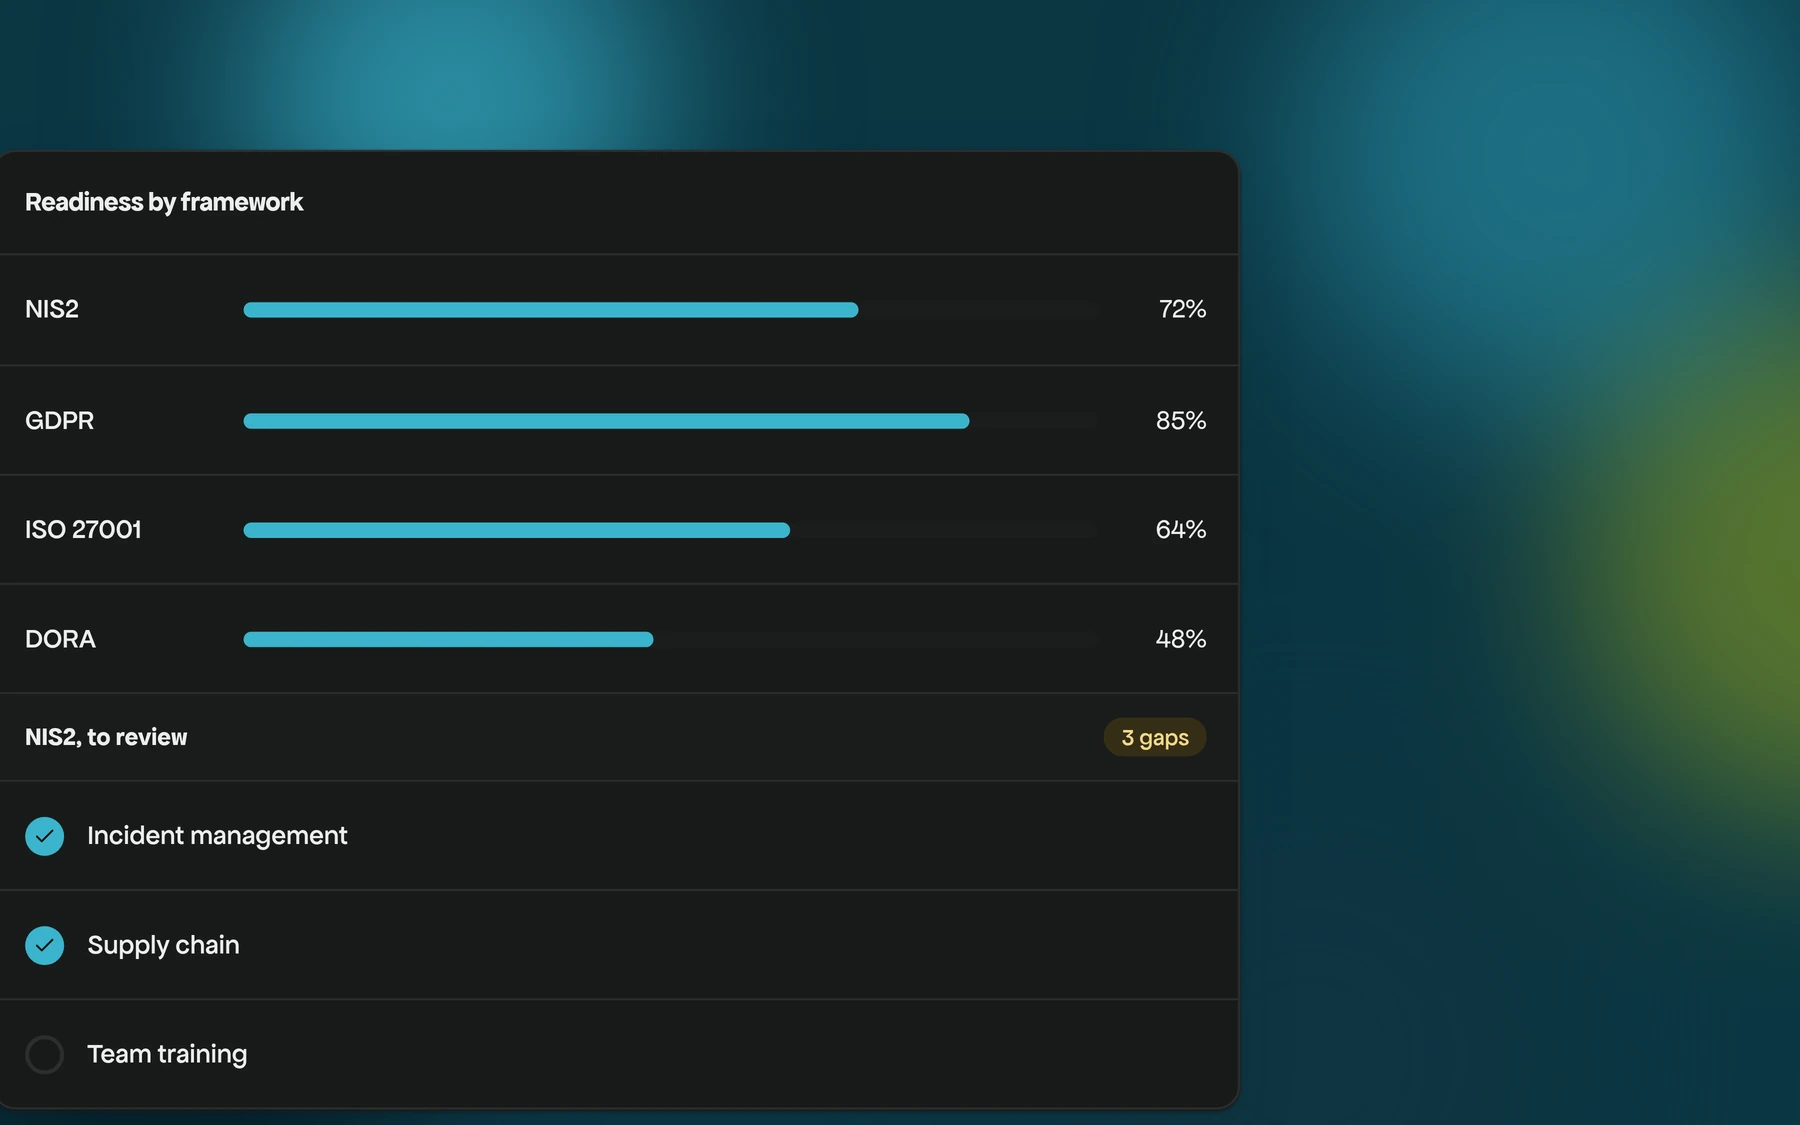
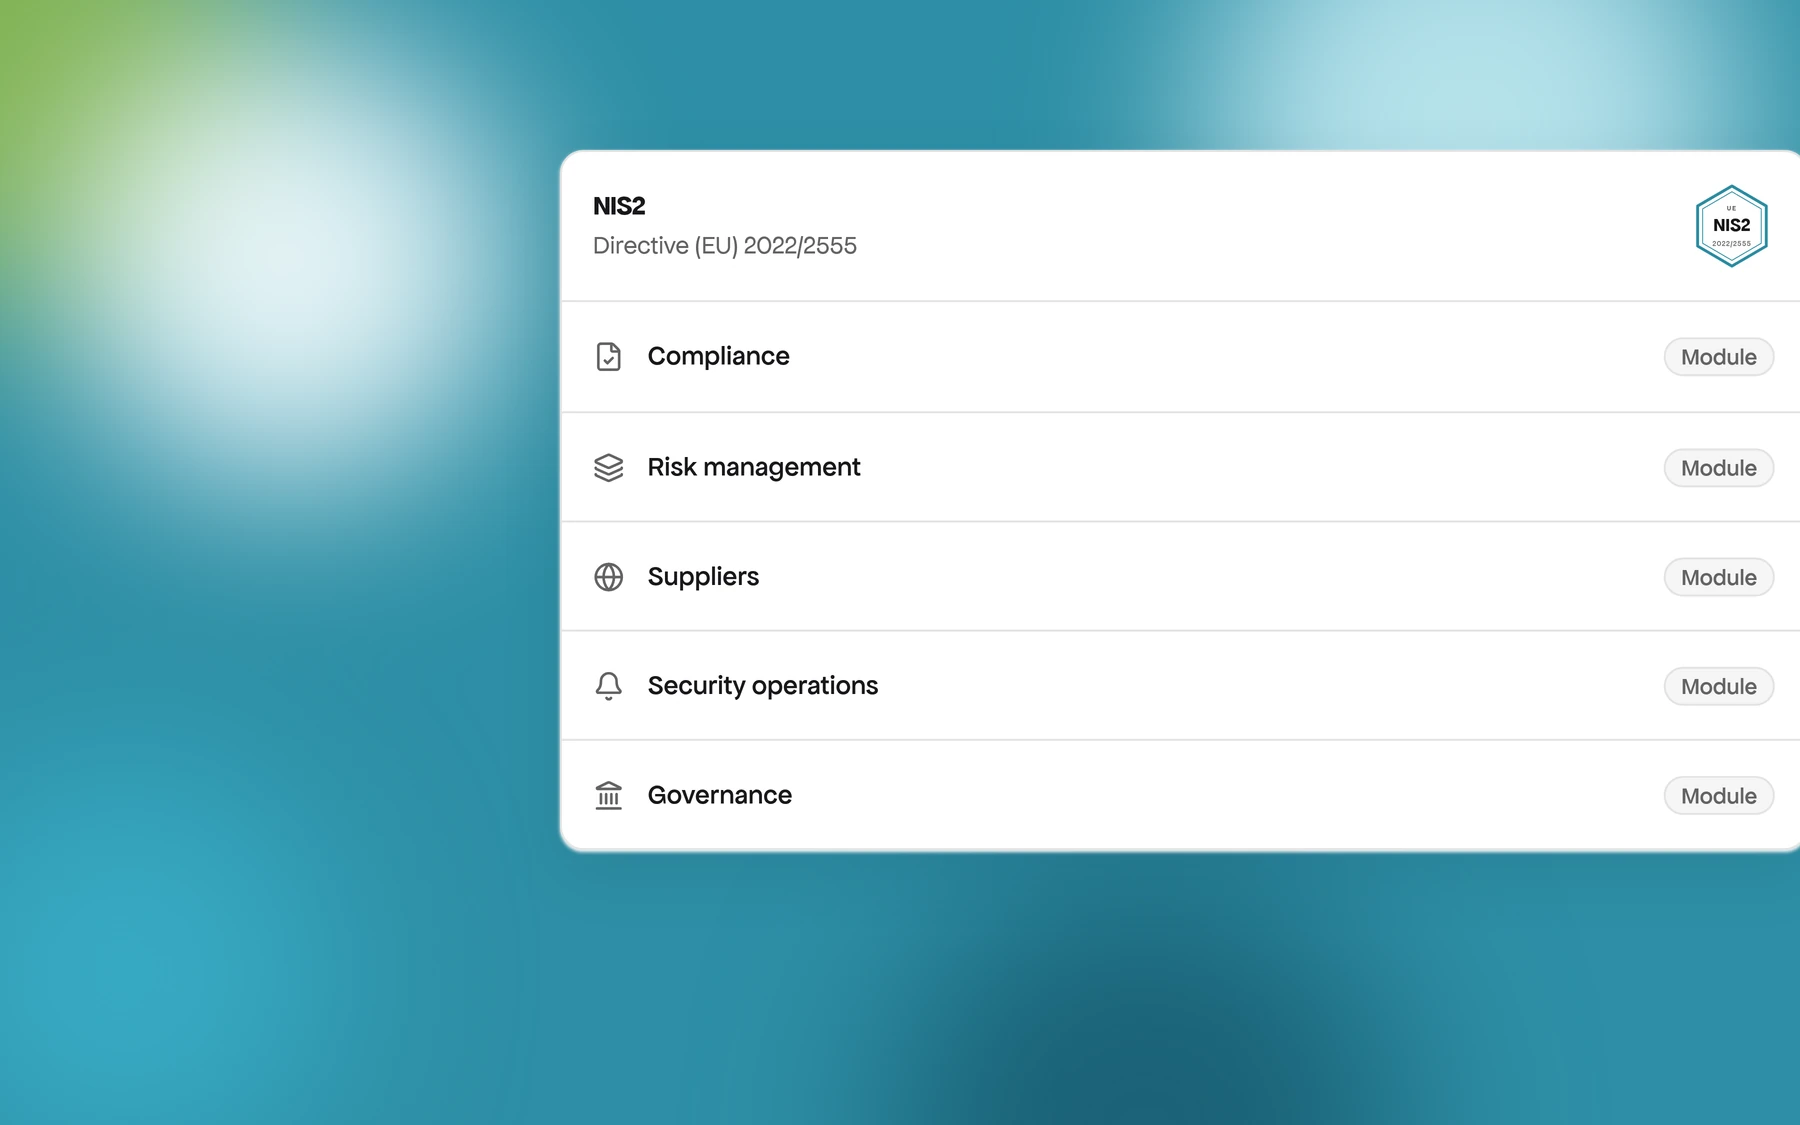
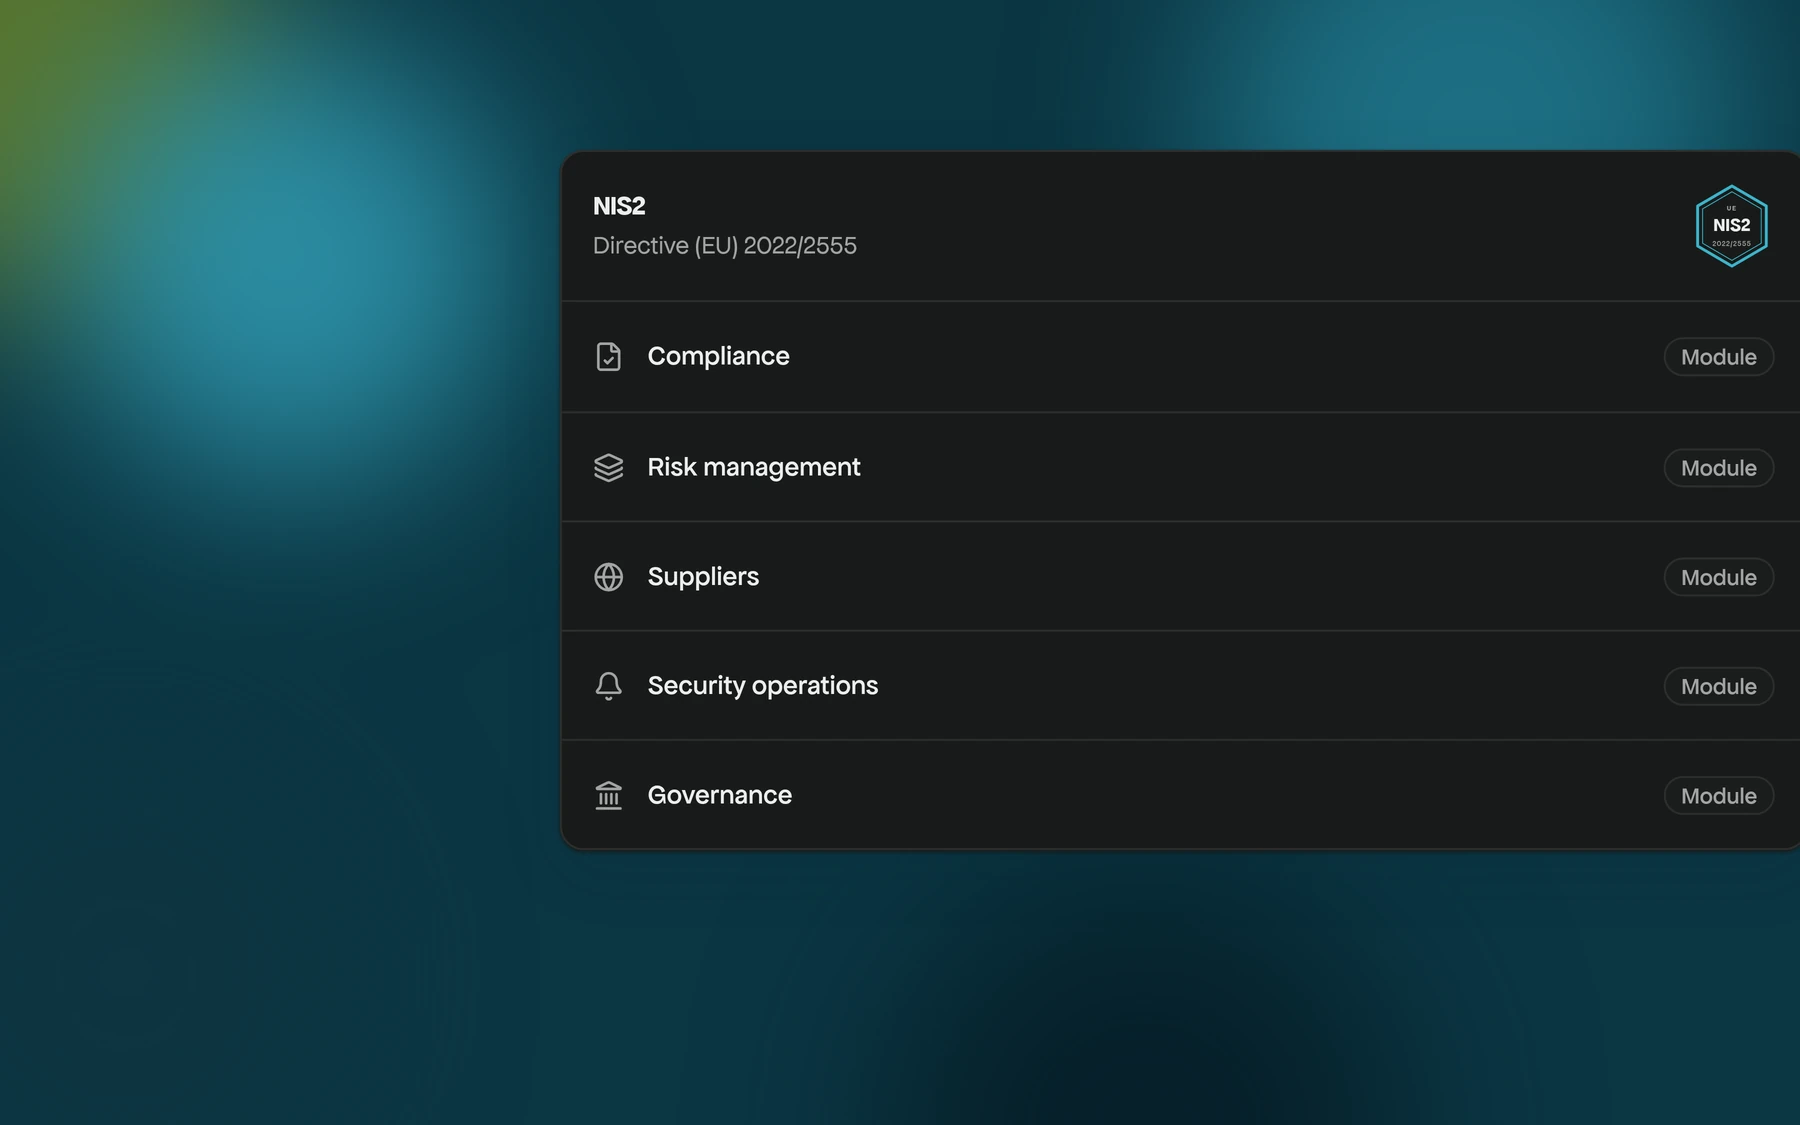
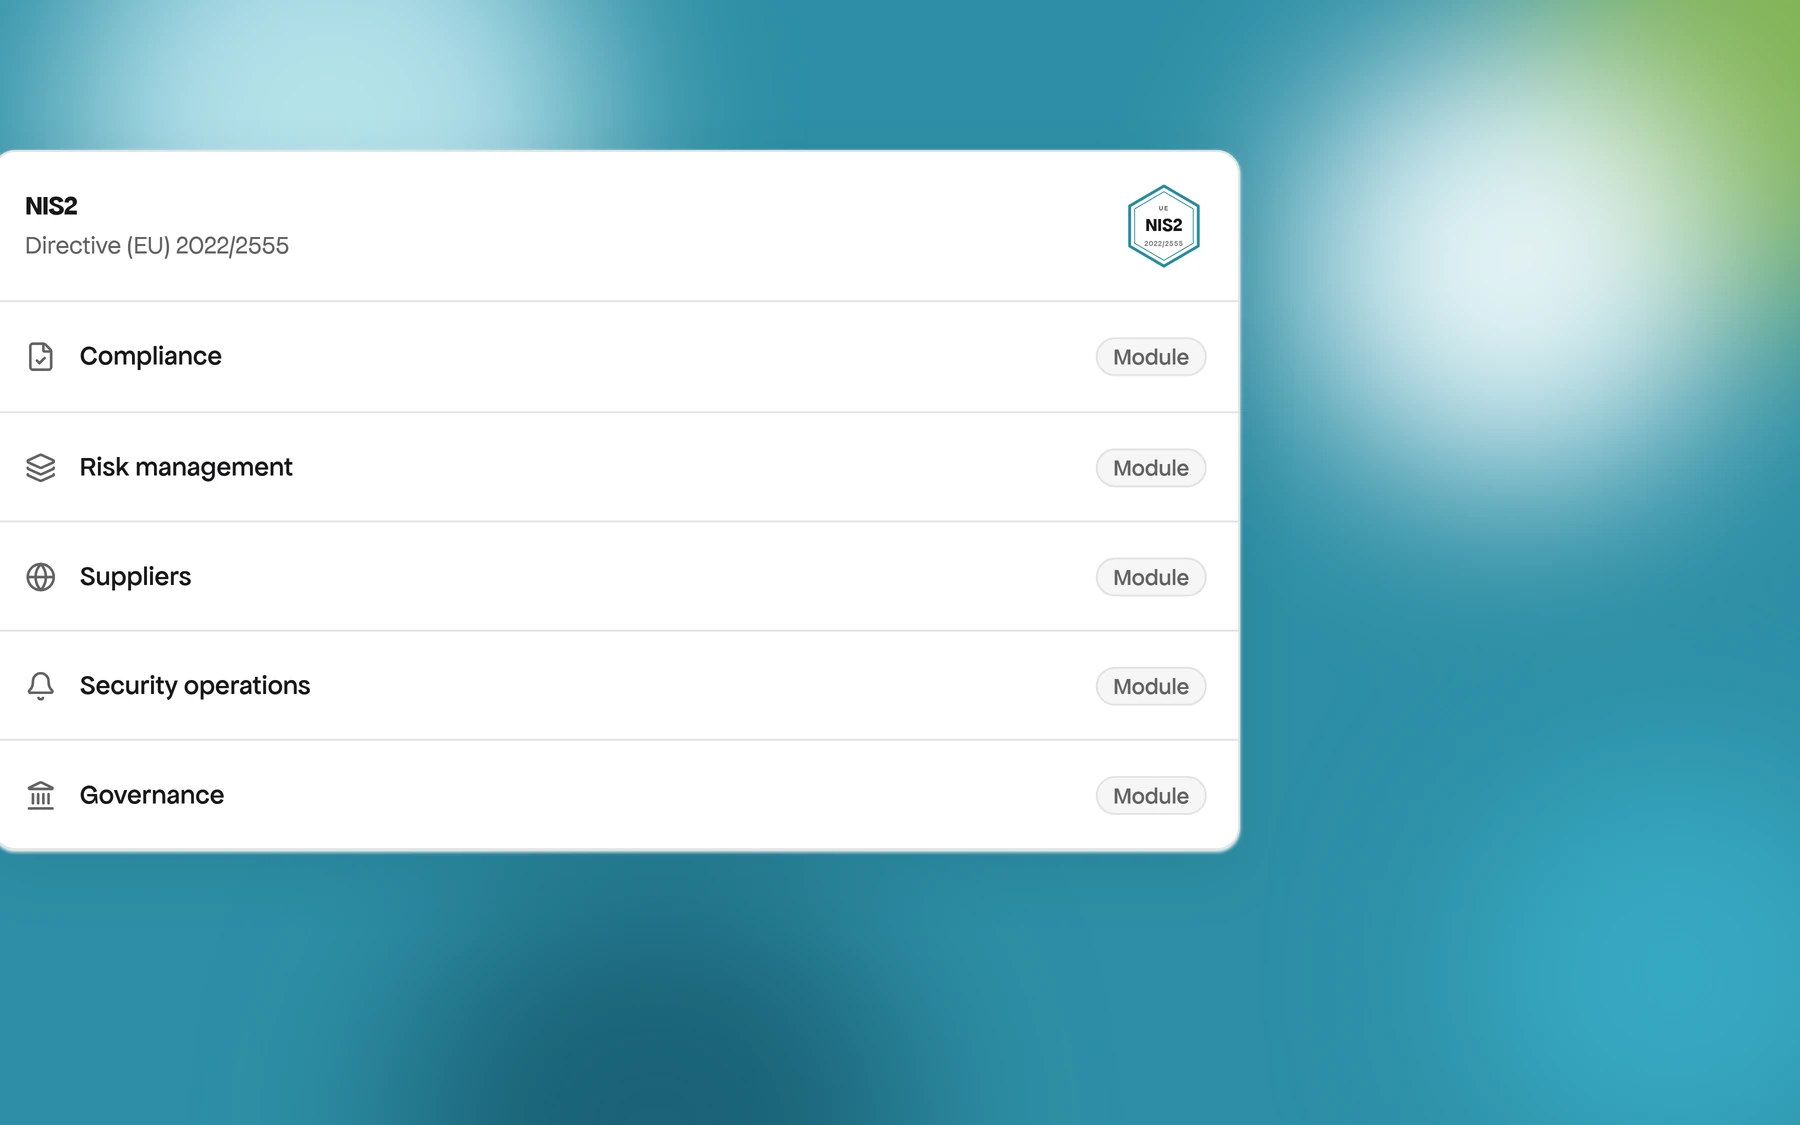
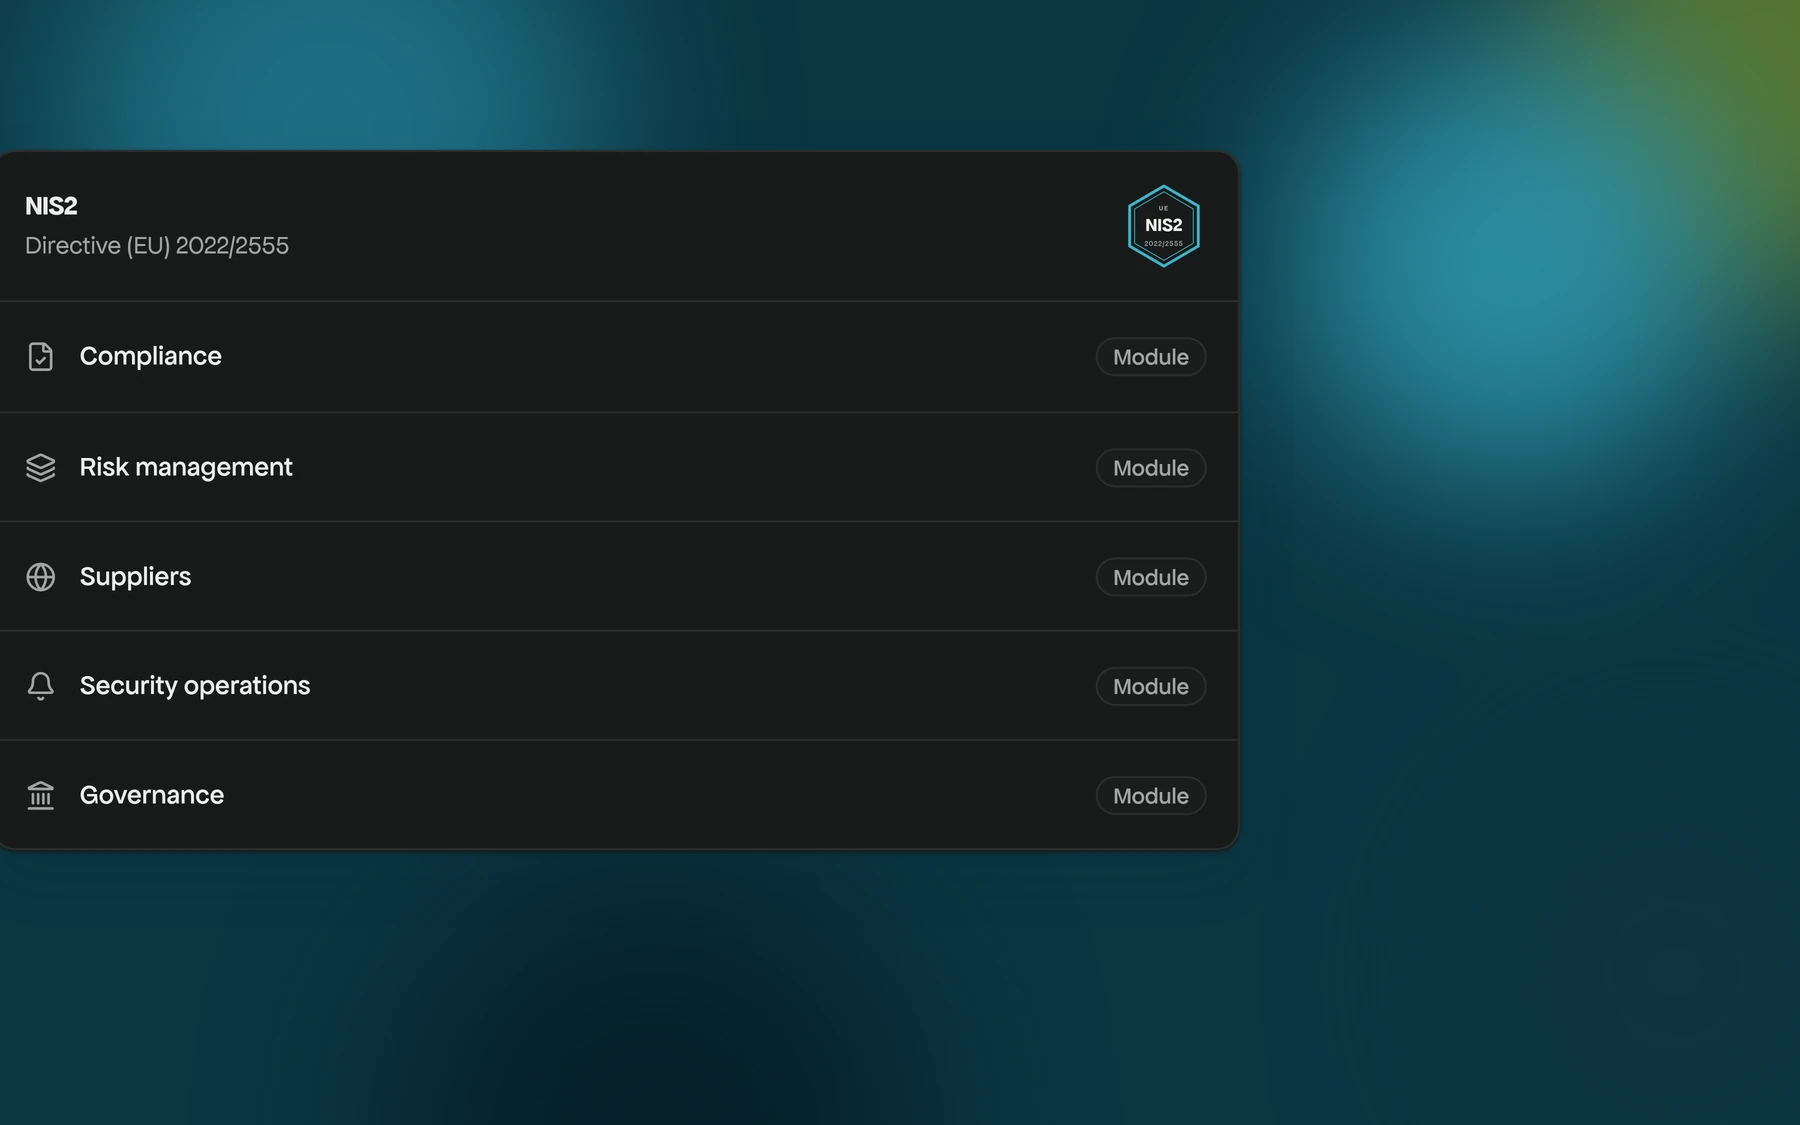
Where you work on it in EterShield
In the documentation
The full control mapping is in the public documentation.
See this framework applied to your organization
In a 30-minute demo we show your gaps and real status.